

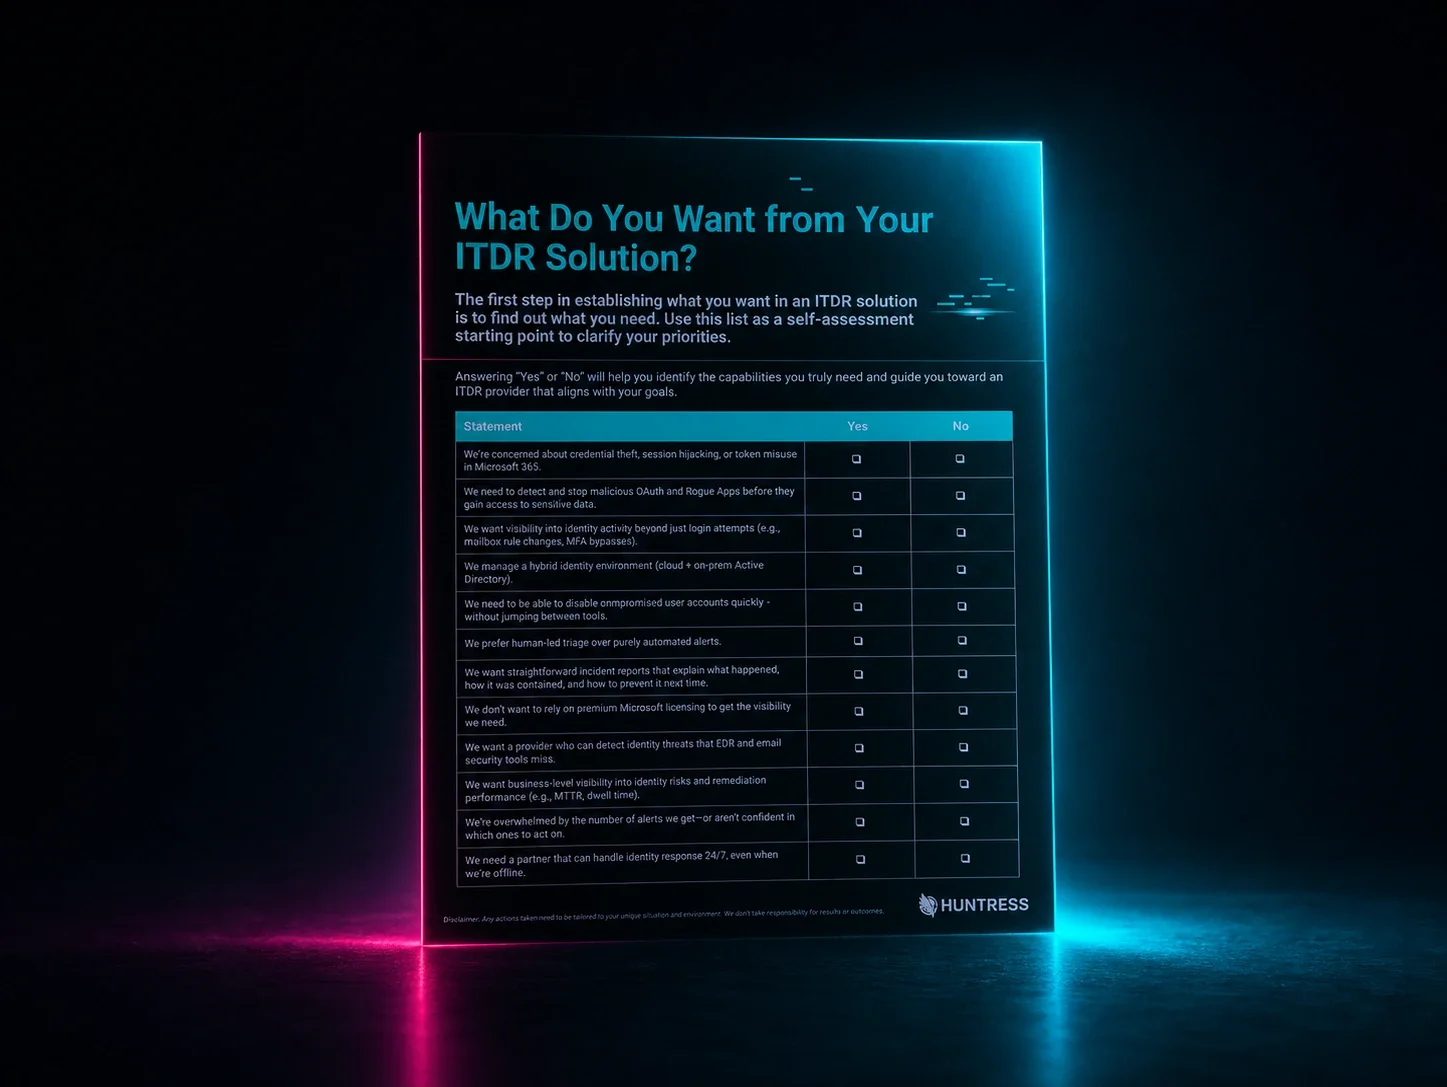
Datasheet
What Do You Want from Your ITDR Solution?
Choosing the right Identity Threat Detection and Response (ITDR) solution starts with understanding what you truly need.
Cybercriminals don’t wait for permission. They sneak in, move fast, and aim for maximum damage. But so do we.
In this session, we break down the real-world attacks our Security Operations Center (SOC) stopped before they could take businesses down. Here’s a taste:
🔥 Credential Theft in Telecom: An attacker quietly lurked for weeks, gathering credentials and mapping the Active Directory.
🔥 Cobalt Strike in Healthcare: A bad actor bypassed MFA in a New Jersey orthopedic network, pivoted with RDP, and prepped a Cobalt Strike beacon to phone home.
🔥 Brute-Force RDP in Food Wholesale: Attackers hammered their way into an RDP server, scanned the network, and modified firewall rules for persistence.
These aren’t hypotheticals: modern attacks happen like this, but we can stop them—together. You’ll walk away with a deeper understanding of:


Related Resources
Choosing the right Identity Threat Detection and Response (ITDR) solution starts with understanding what you truly need.
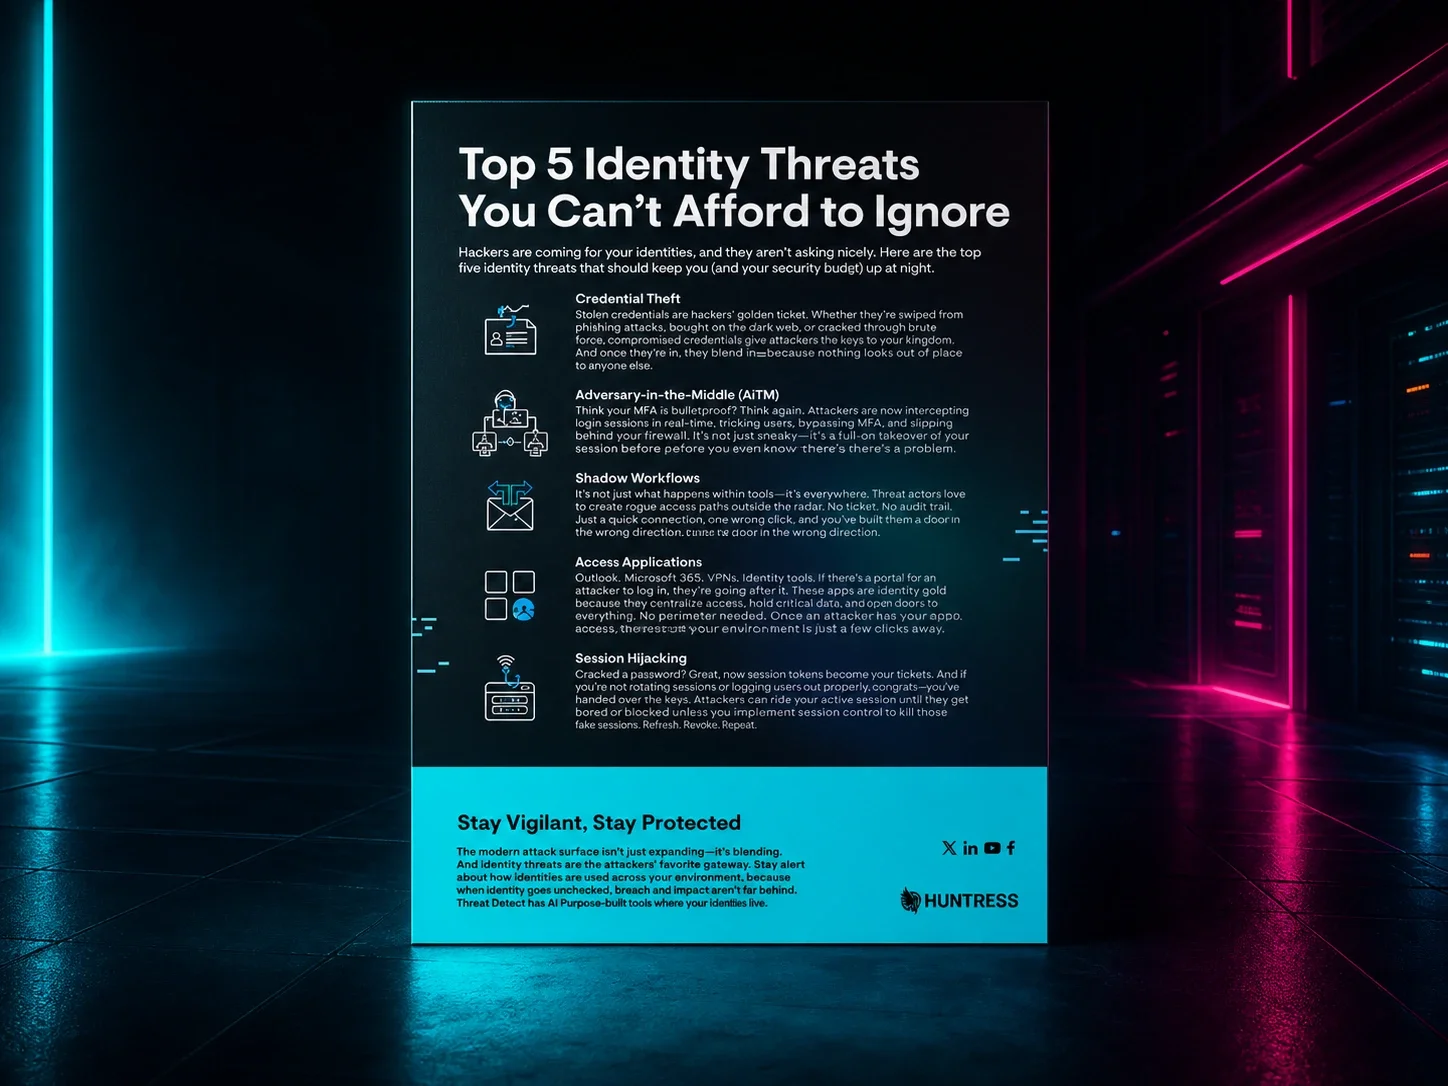
Cybercriminals are coming for your identities—and they’re not playing nice. Learn more about credential theft, AiTM, shadow workflows and more.
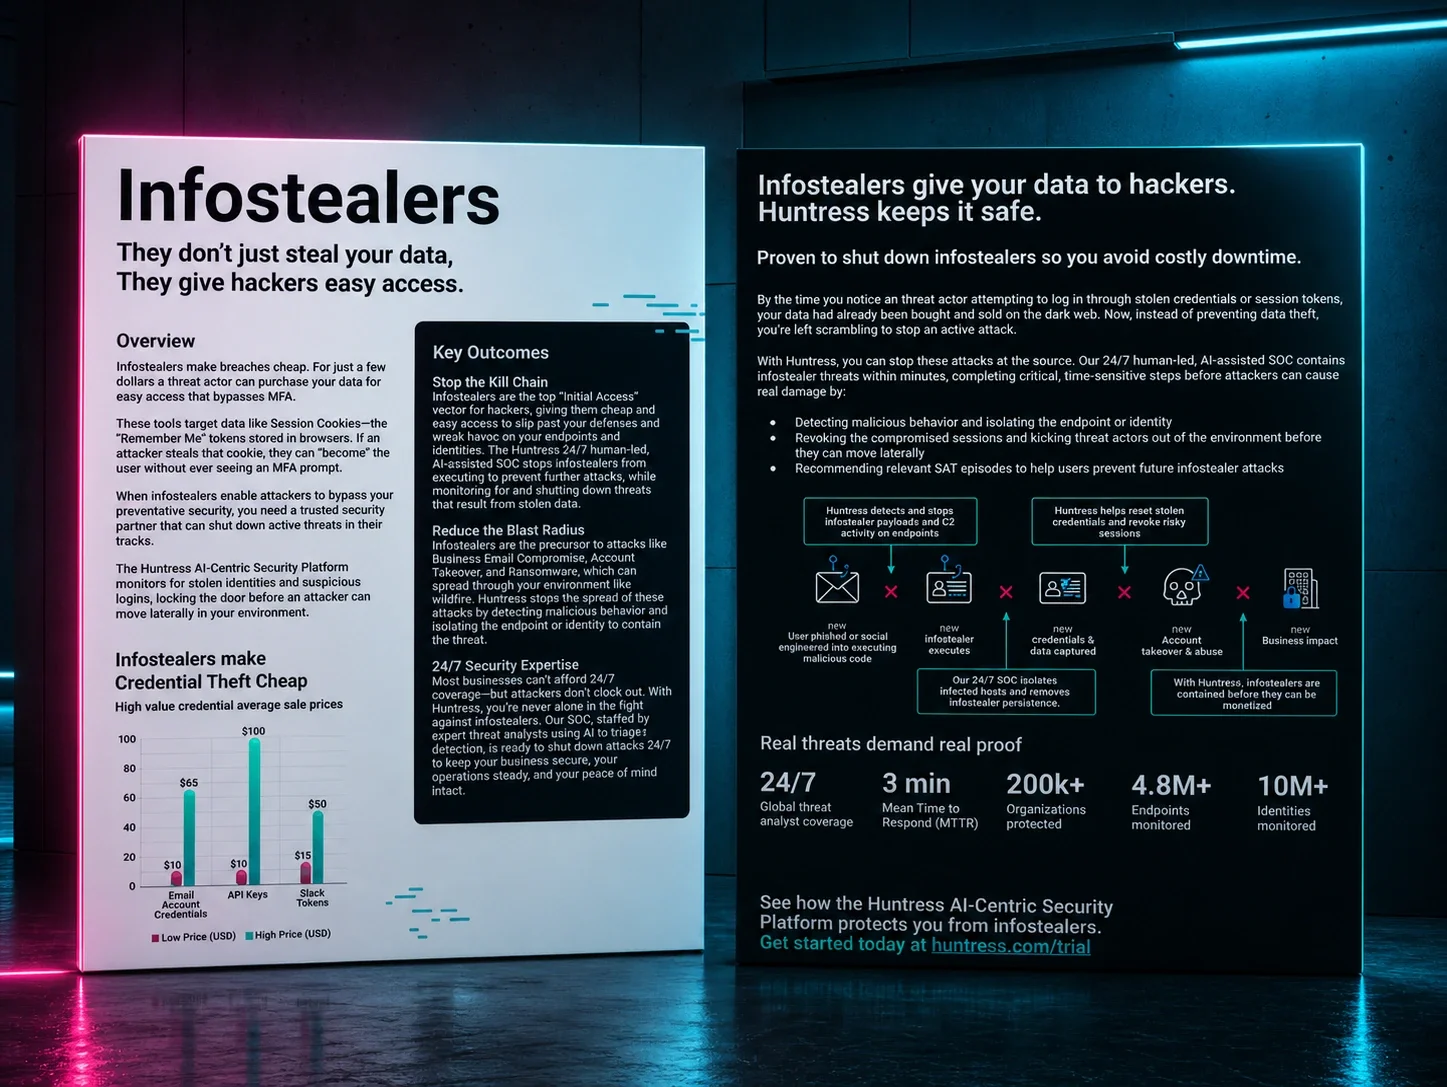
Block infostealers, credential theft and account takeover with Huntress’ AI-driven security platform and 24/7 human-led SOC that shuts down active threats fast.
Learn how session hijacking lets cybercriminals duck under the velvet ropes of Multi-Factor Authentication (MFA) and stroll straight into your private data.

As security teams turn to AI tools, explore where AI can save your team time and what pitfalls are worth avoiding.
Learn how scattered public data turns into cyber threats. Watch Huntress Truman Kain and Cybersecurity Girl Caitlin Sarian break down identity risks.
Not all threats come from malware—some come from legitimate apps. Traitorware - a type of Rogue Apps - is what we call OAuth application abuse in Microsoft 365. Attackers exploit real, trusted apps—like EM Client—to gain persistent access to inboxes, siphon data, and evade detection.
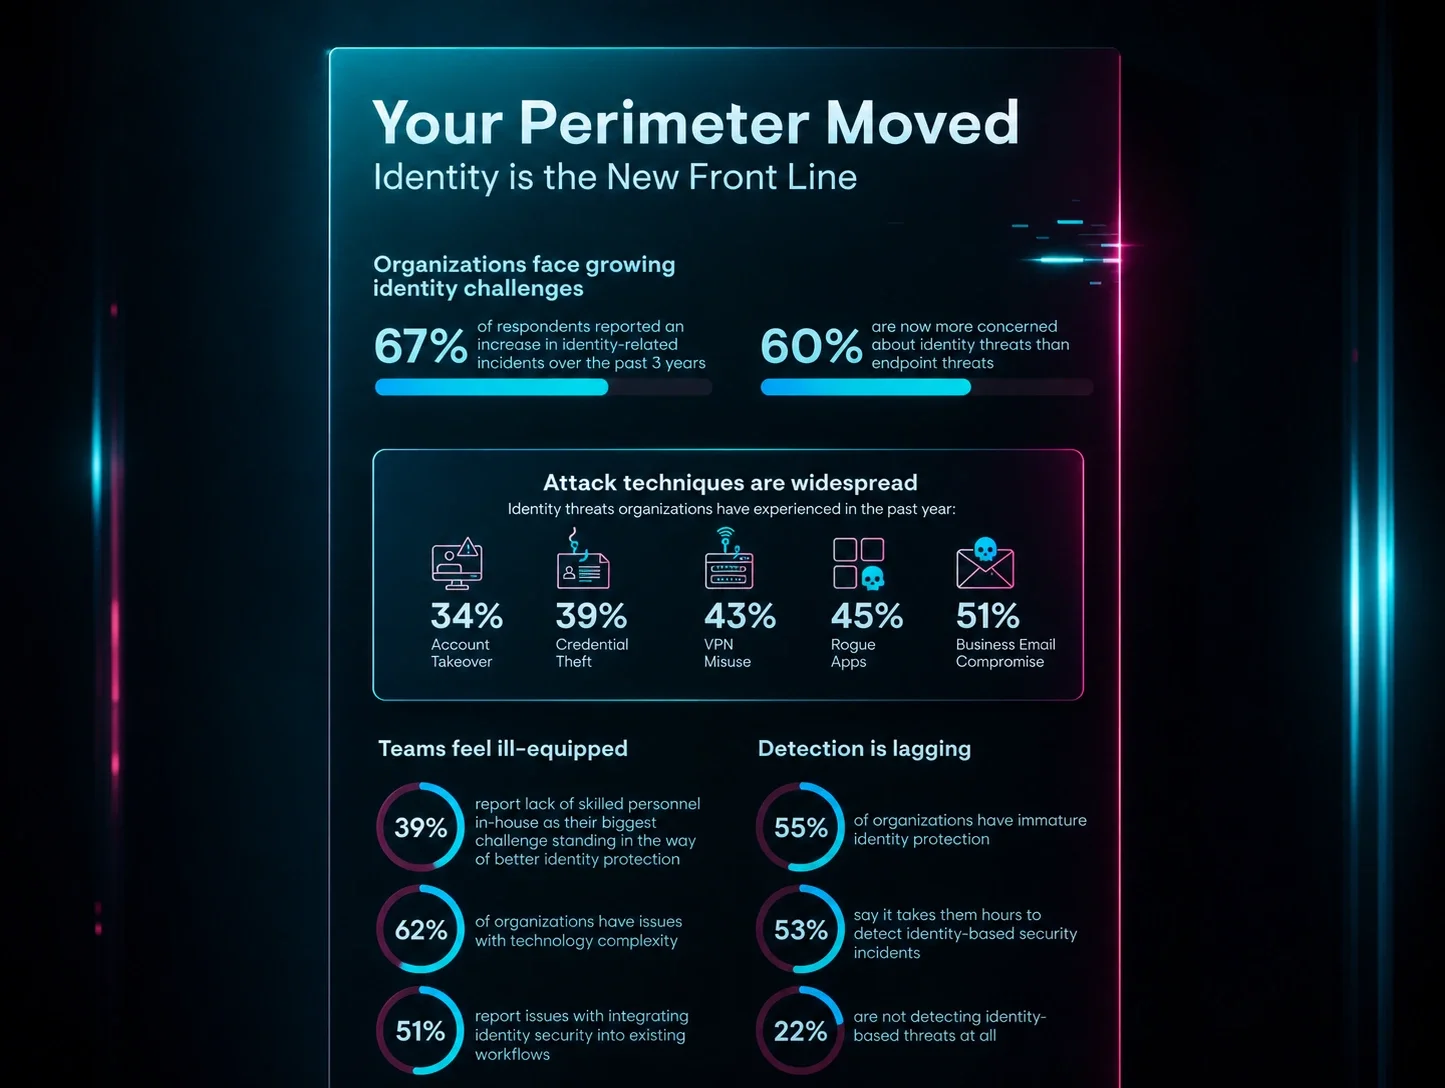
Hackers are changing up their tradecraft. Instead of wasting time breaking into your network the hard way, they’re going after your email and cloud infrastructure with identity-based attacks. The security perimeter is shifting—and identity is the new front line.
Hackers have a new favorite flavor of tradecraft: identity. Hear about what identity attacks are, how they work, and how ITDR protects businesses.
