Once inside, attackers are quick to act
Training and hardening reduce risk, but don't eliminate it. When attackers find a way into a target environment, they move fast – installing persistent footholds, running infostealers, setting up malicious email forwarding, and even deploying ransomware.
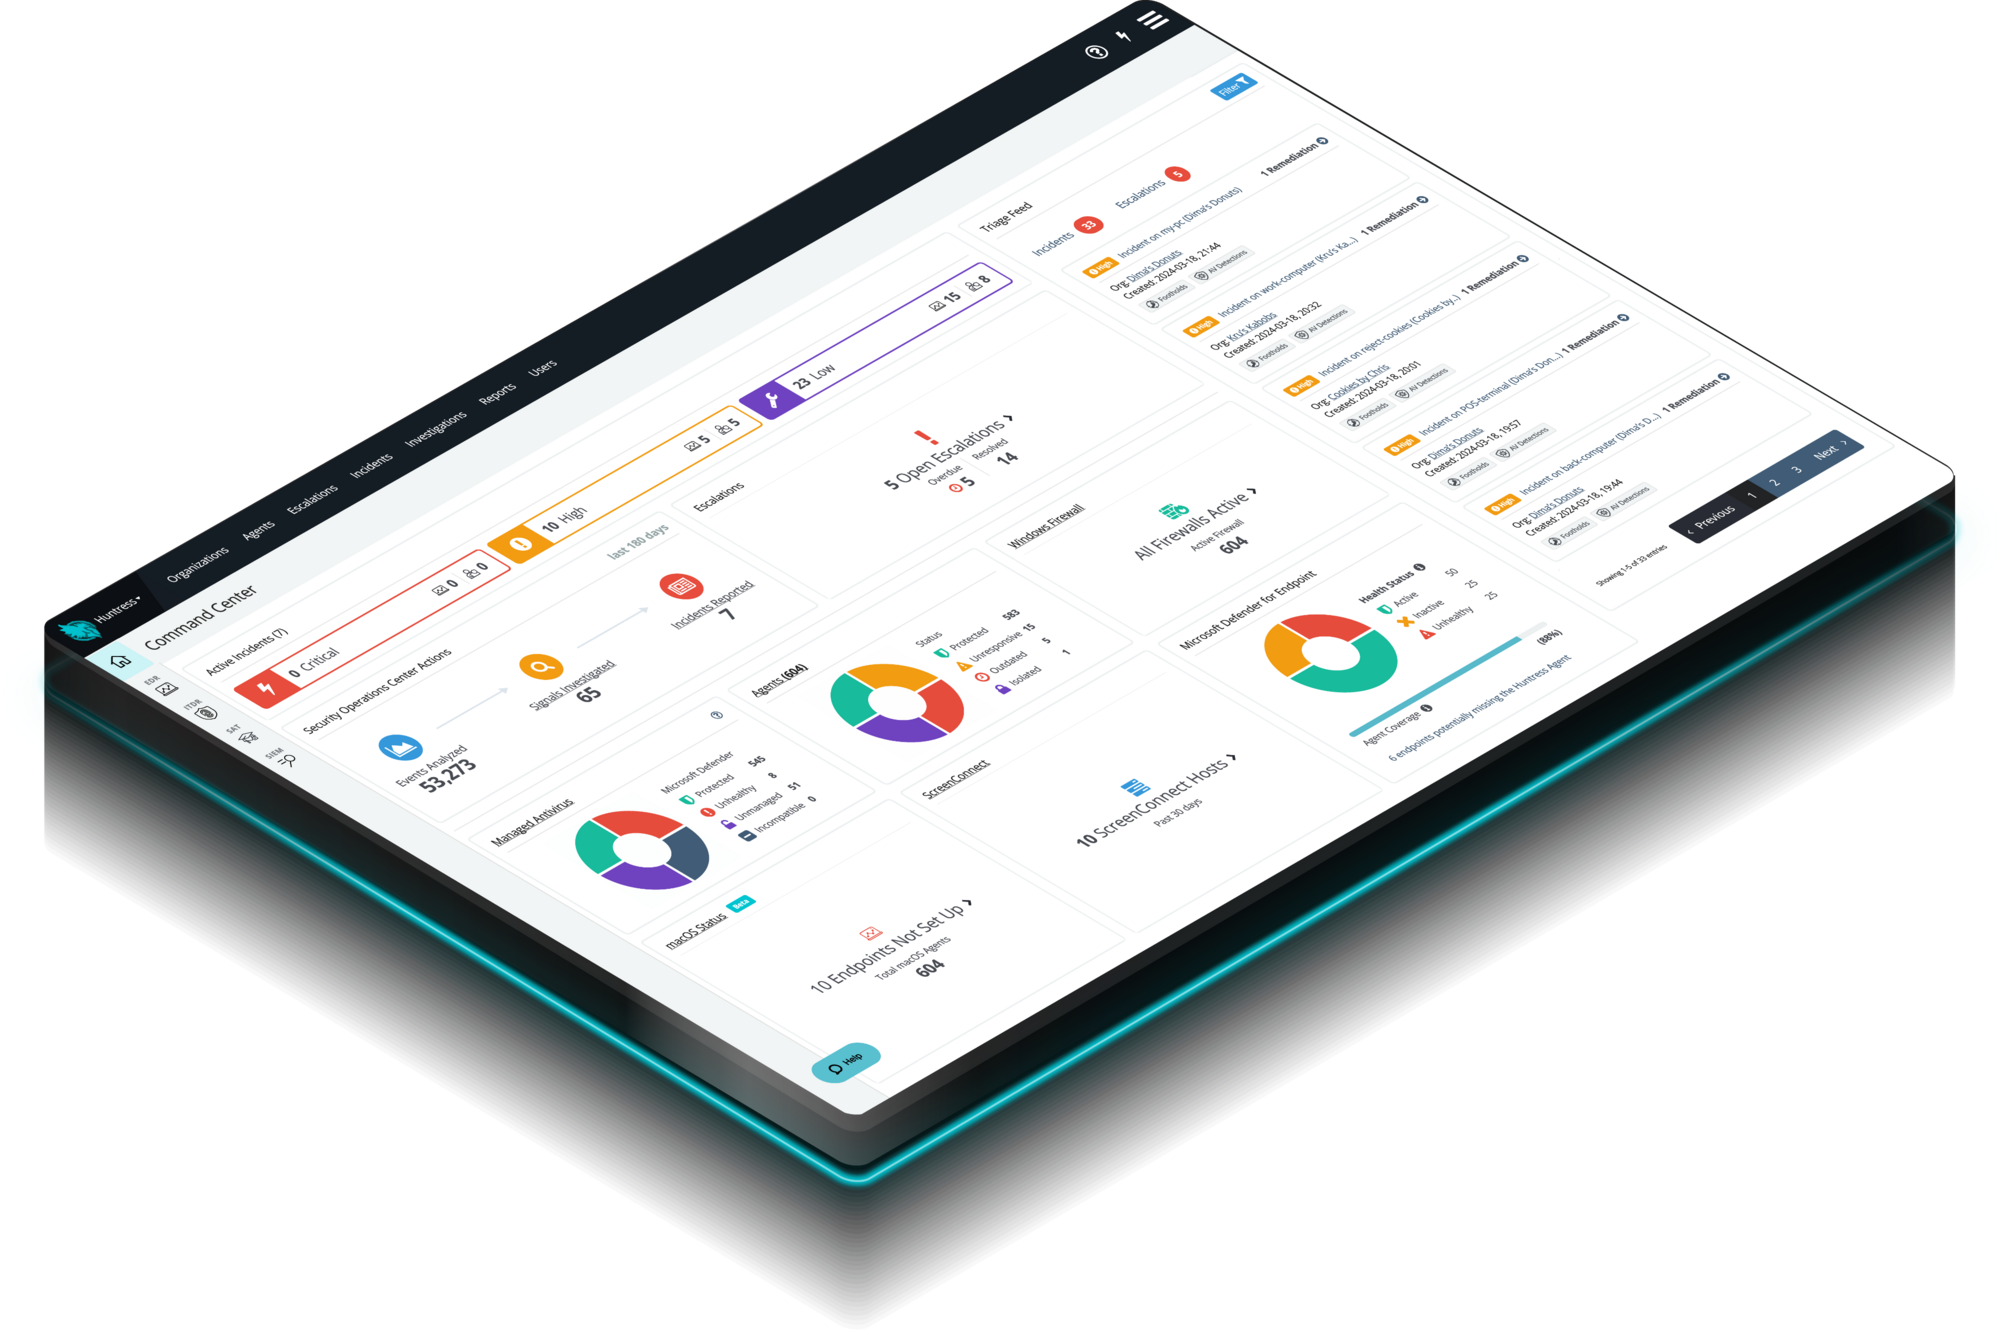
Huntress Managed EDR is built to catch exactly that kind of activity on the endpoint: unauthorized RMM installs, infostealer execution, and the malware that follows, stopped before it can spread further.
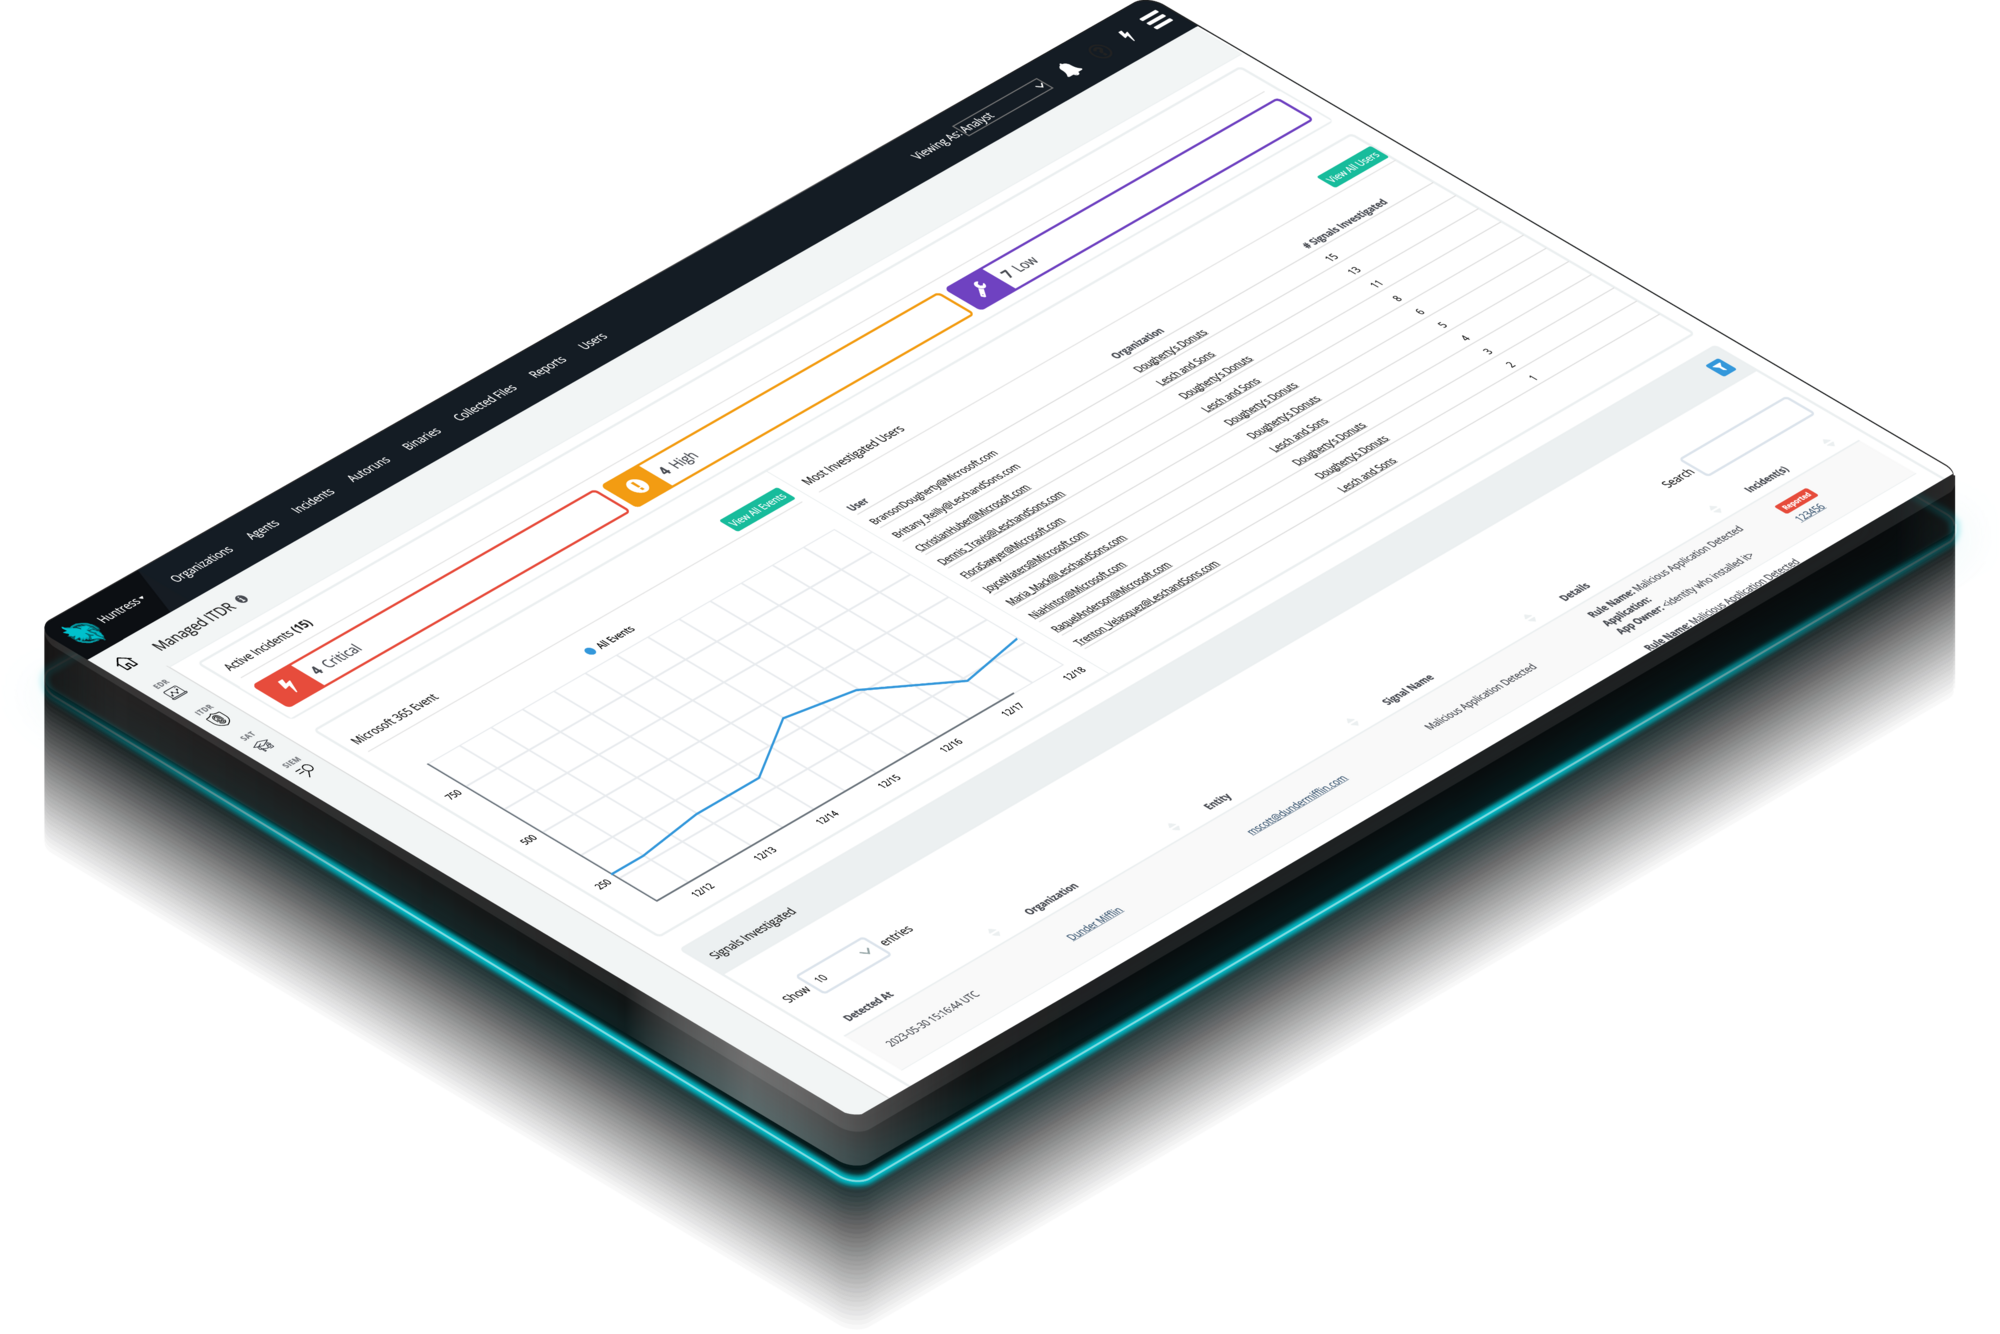
Because attackers just as often go after identities, Managed ITDR watches Microsoft 365 and Google Workspace for fallout too: rogue mailbox rules, suspicious logins, and stolen session tokens, so a compromised account gets contained before it’s too late.
And because attackers don't limit themselves, Managed SIEM monitors the spaces in between and earlier in the attack chain. By analyzing operating logs, firewalls, and cloud logs, it catches the lateral movement and infrastructure changes that signal a broader attack.