

Blog Post
Getting to the Crux (Ransomware) of the Matter
Huntress spotted a new ransomware variant claiming ties to the BlackByte group. Crux has appeared in three separate incidents — here's what analysts found and the indicators of compromise.
Huntress spotted a new ransomware variant claiming ties to the BlackByte group. Crux has appeared in three separate incidents — here's what analysts found and the indicators of compromise.
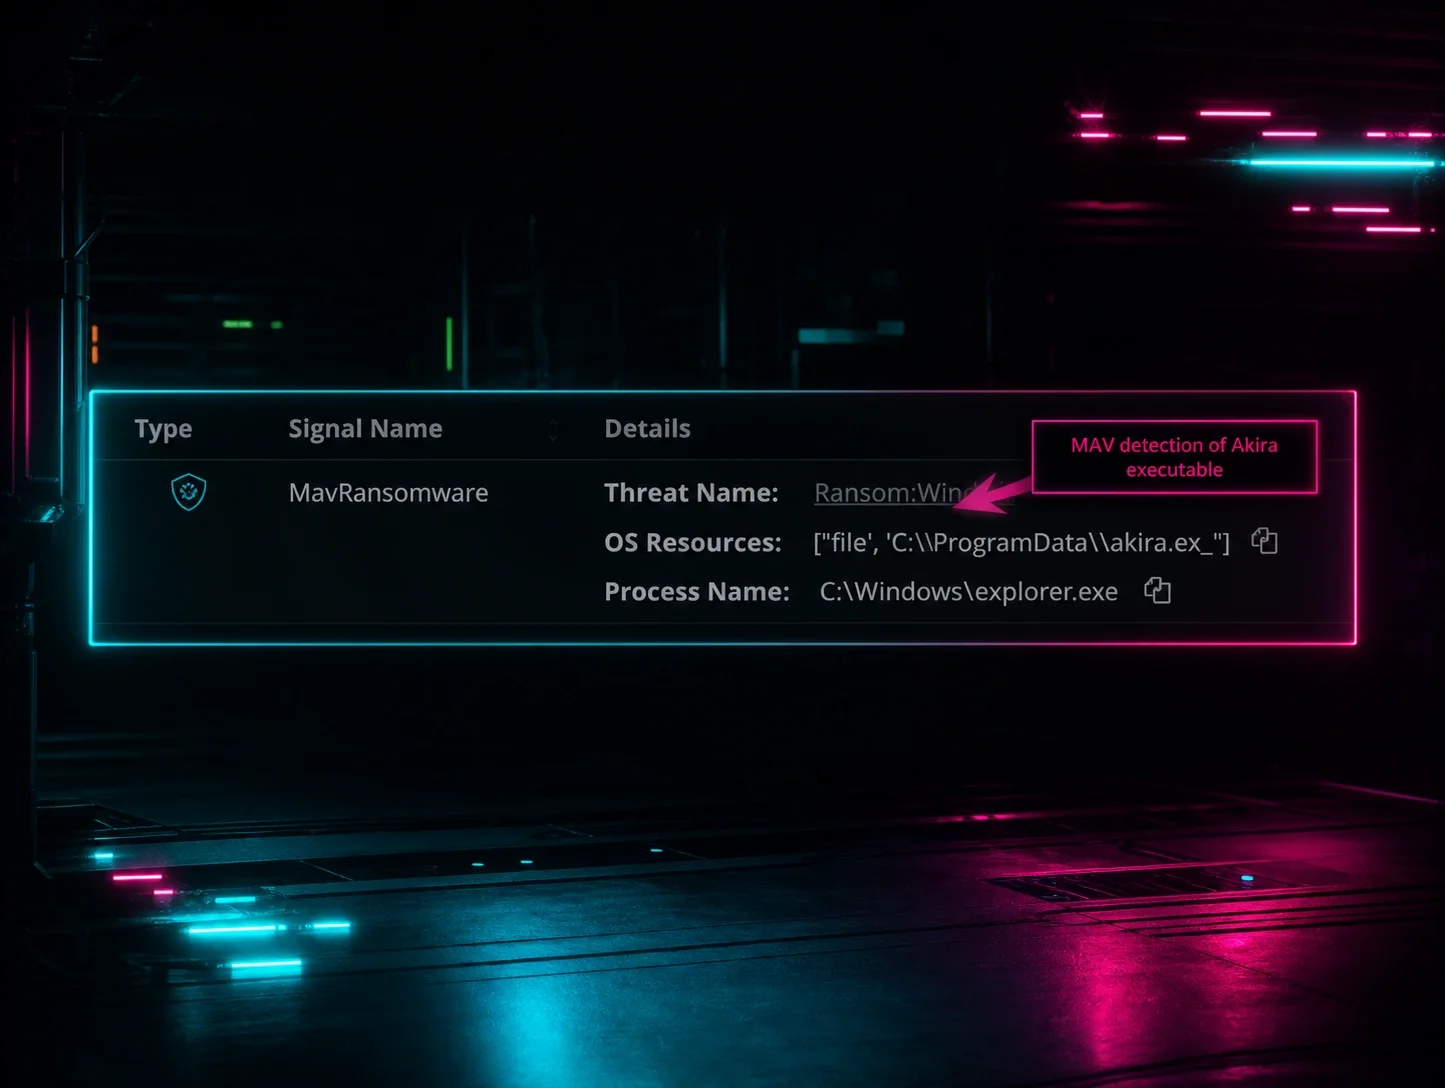
When a threat actor compromises an MSP's RMM tool, every customer on that platform is a potential target. Huntress documents Part II of a campaign designed to hit MSP customers in bulk.
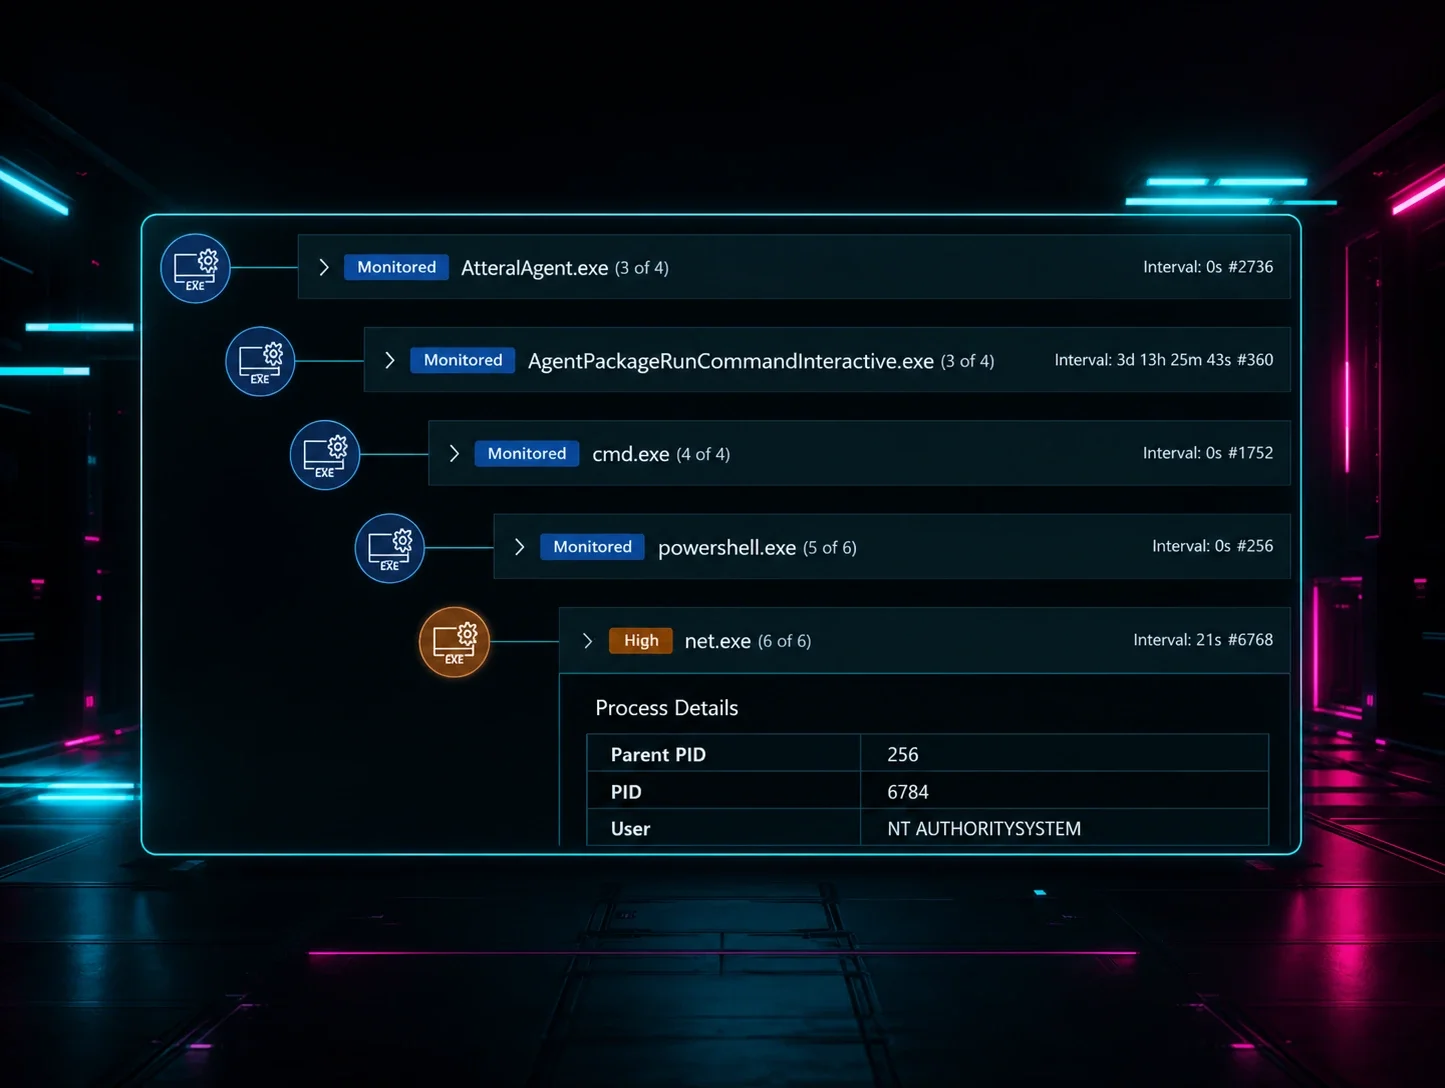
MSP RMM tools are a convenient way to manage customer environments — and an equally convenient entry point for attackers targeting those same customers. Part I of the investigation starts here.
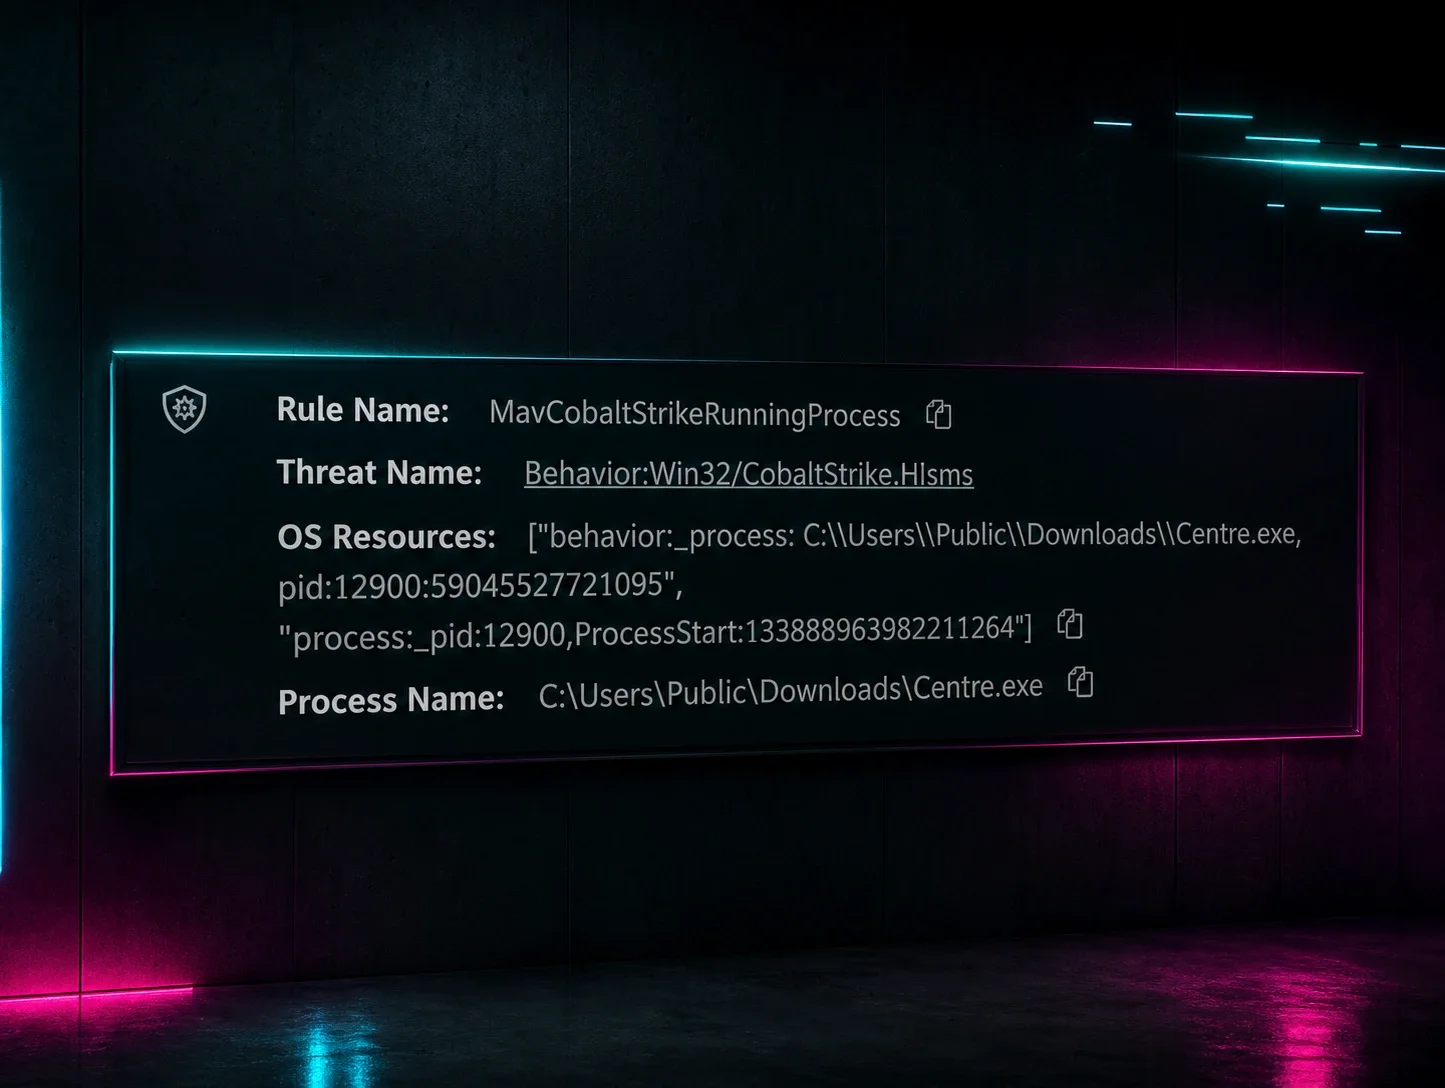
The security community keeps saying threat actors always change their tactics. Analysts who actually track TTPs over time have a different perspective — and the data to back it up.
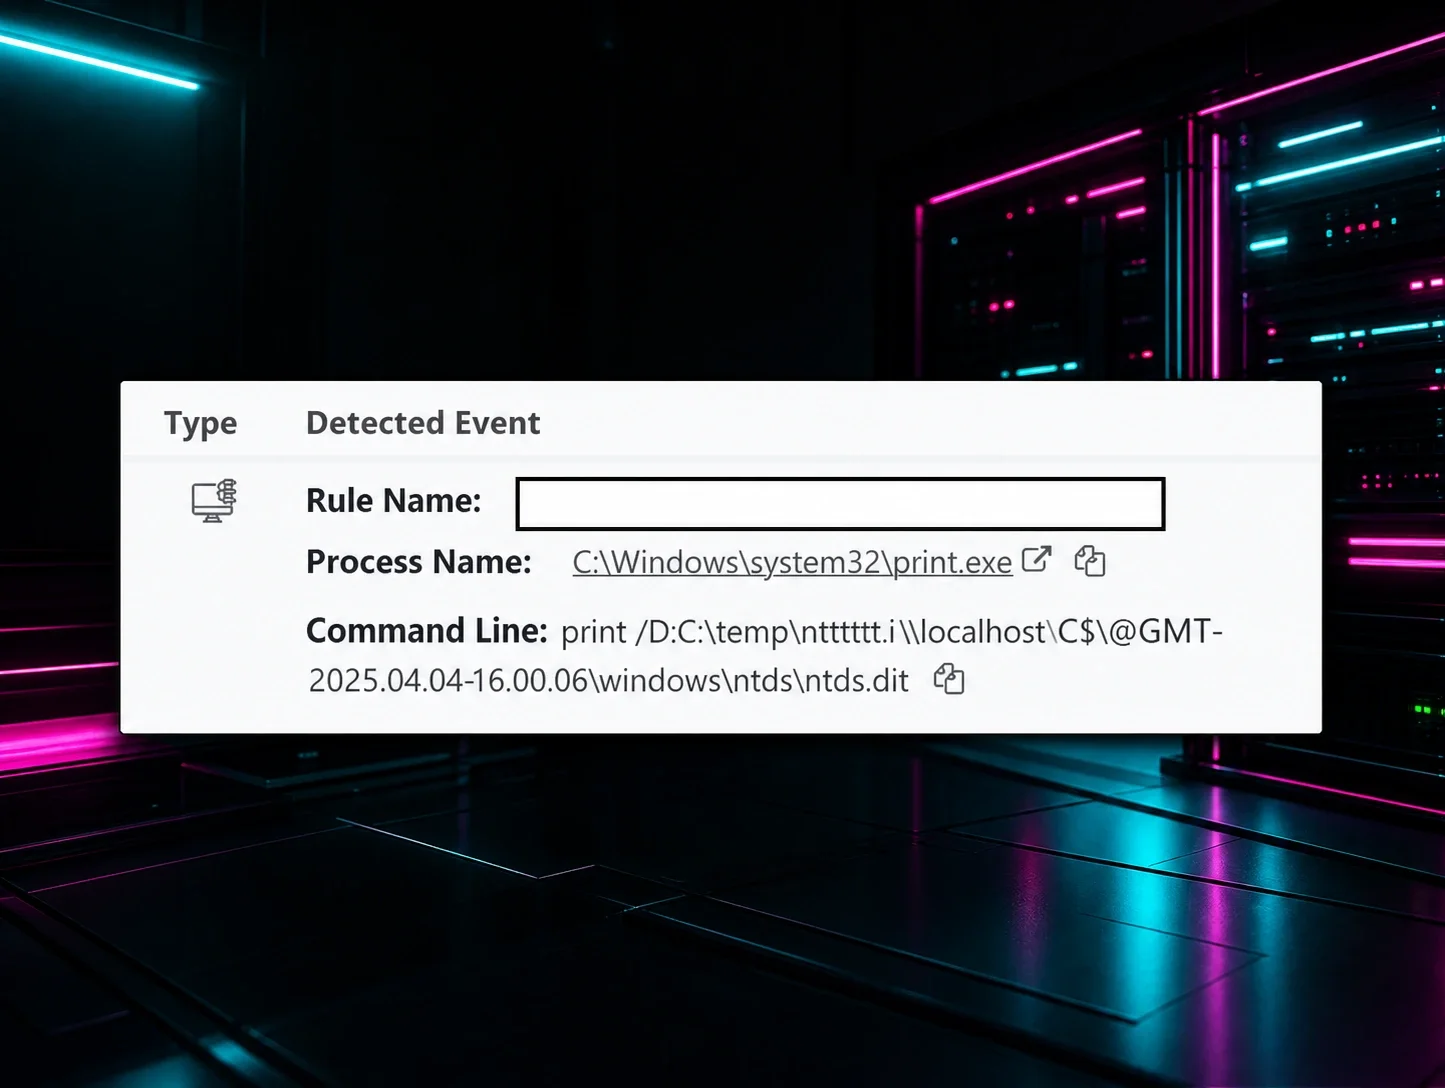
Credential theft is how initial access becomes lateral movement. Part II illustrates the techniques in detail, showing what each one looks like in actual security telemetry.
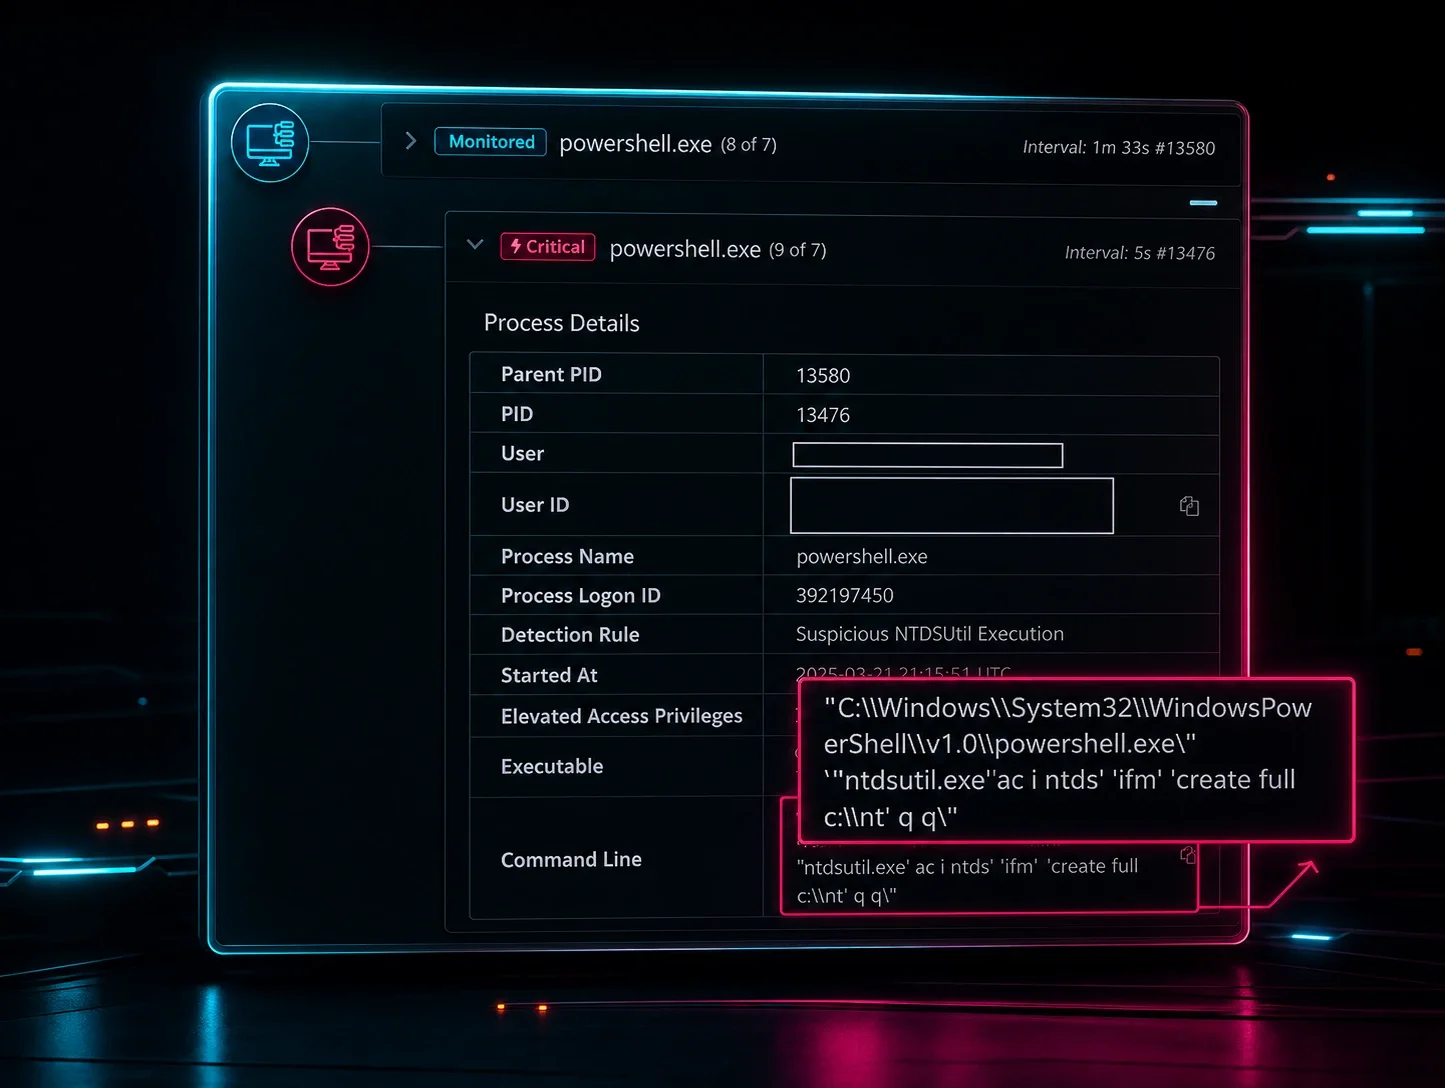
Credential theft is how attackers turn a foothold into full access. This primer covers the techniques, the tools, and the path from initial access all the way to lateral movement.
