

Blog Post
Reports of SIEM's Death Have Been Greatly Exaggerated
SIEM isn't dead... its bloated pricing model is. Discover why legacy models need to go, how AI fits in, and how to build a smarter, cost-effective security logging strategy.
SIEM isn't dead... its bloated pricing model is. Discover why legacy models need to go, how AI fits in, and how to build a smarter, cost-effective security logging strategy.

UPDATED: Critical vulnerability in N-able N-central gives attackers unauthenticated, "god-mode" access to the RMM console.
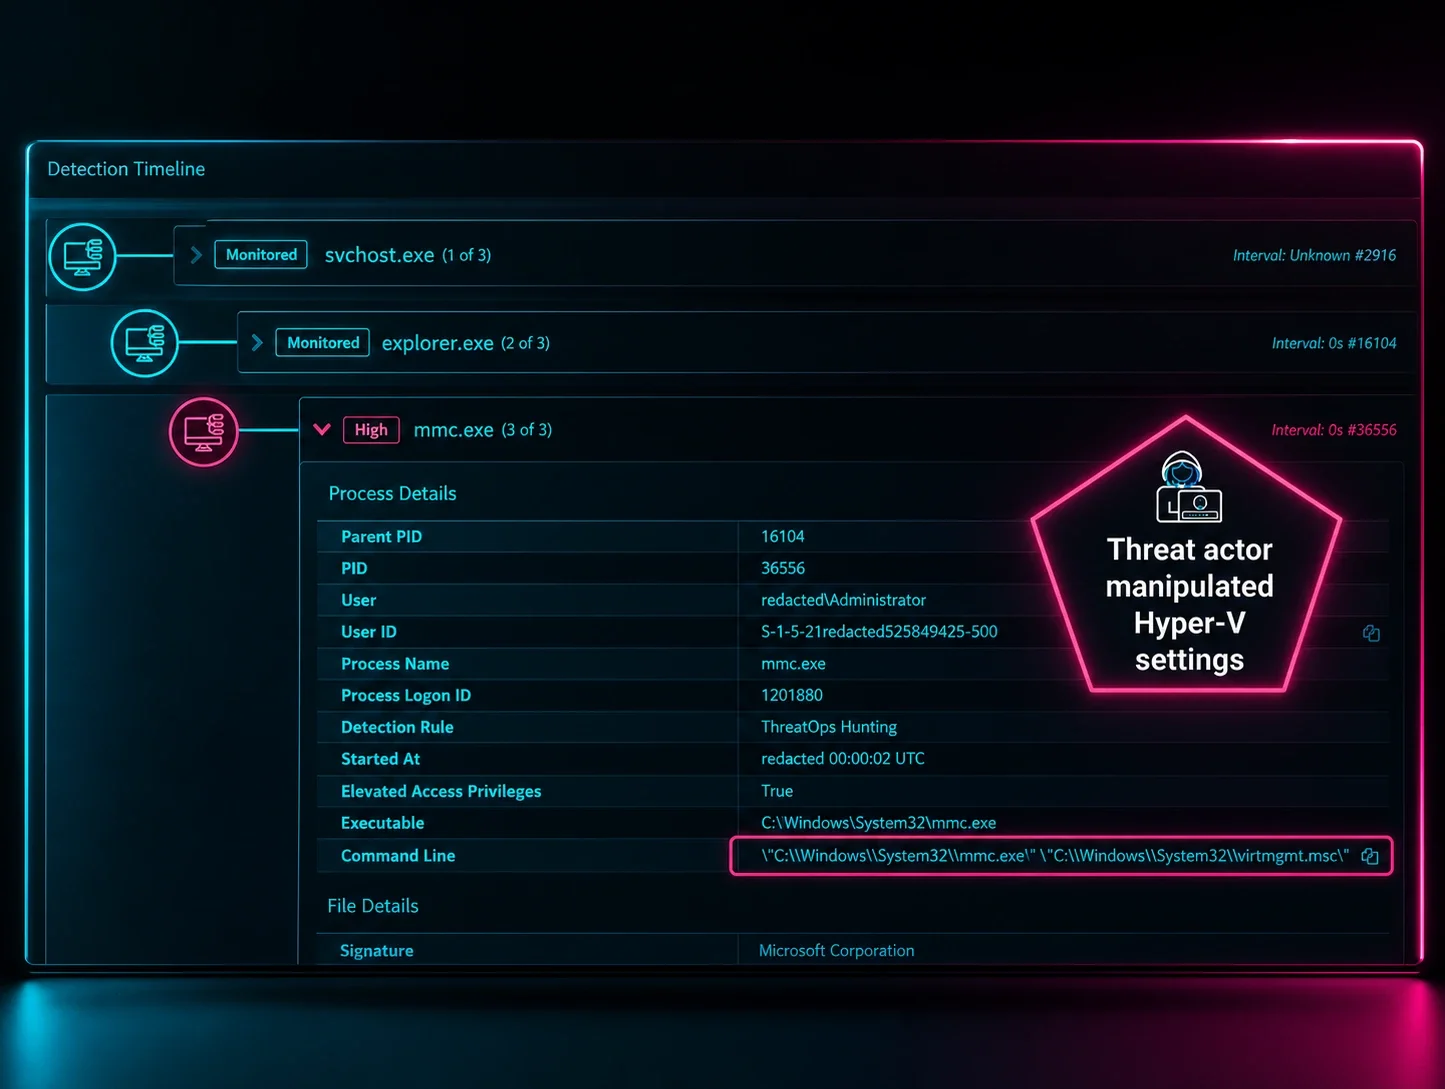
A single breach at the hypervisor layer puts every virtual machine at risk simultaneously and most security tools are blind to it. Here's how to actually harden ESXi against ransomware.
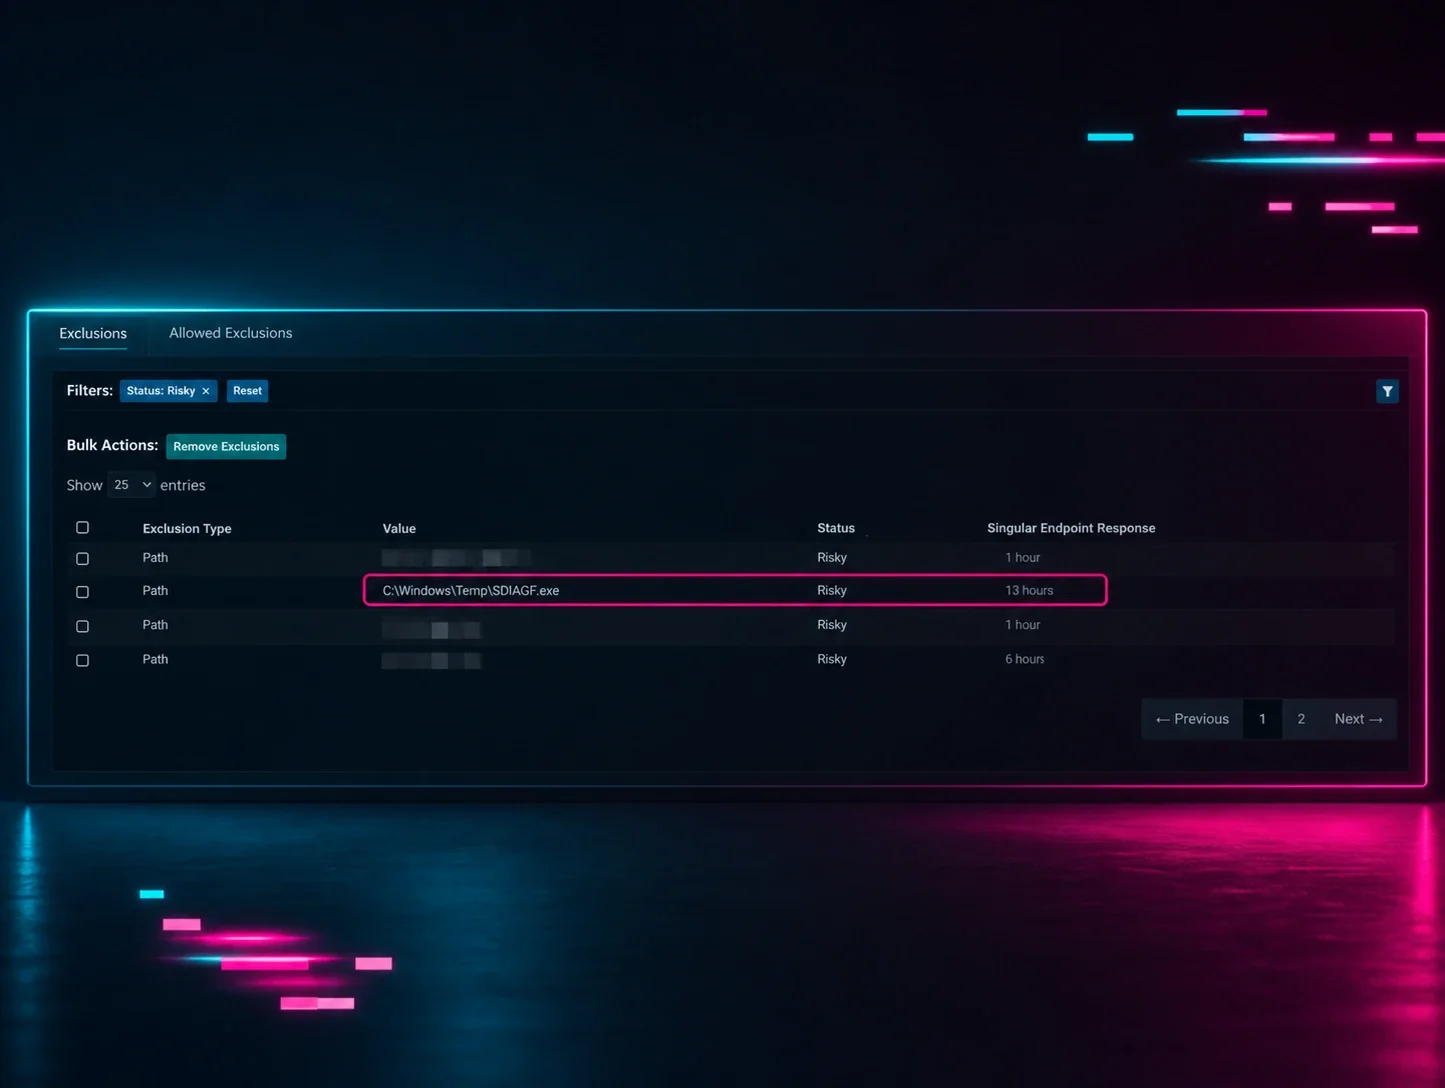
A Huntress TAM doing a routine account review found something that wasn't supposed to be there: unauthorized surveillance tools running quietly in a partner's environment. Here's what happened.
