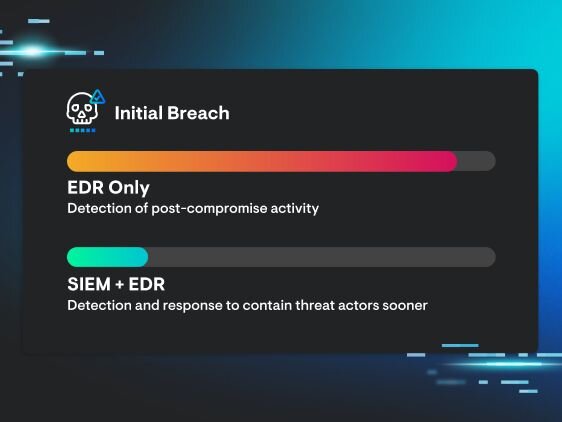
“We'll get to SIEM next year.” That decision has cost a lot of businesses a lot of money. Every quarter you wait is a quarter of activity you can't see and can't prove—and threat actors are counting on exactly that blind spot.
Here's why centralized visibility and logging can't sit on the back burner.
The risk of waiting
You can't investigate what you didn't log. When an incident hits, missing history means missing answers.
Blind spots compound. The longer you go without visibility, the more an attacker can do damage unseen.
Recovery is slower and costlier when you're piecing together what happened after the fact.
The compliance clock is ticking
More frameworks and cyber-insurance policies now expect centralized logging and monitoring. Waiting doesn't just raise your risk. It can put coverage and compliance out of reach when you need them most.
A SIEM you can stand up without the pain
The usual reason teams stall is cost and complexity. Managed SIEM takes both off the table—predictable pricing and managed response from the Huntress SOC, so 'later' can become 'now.'
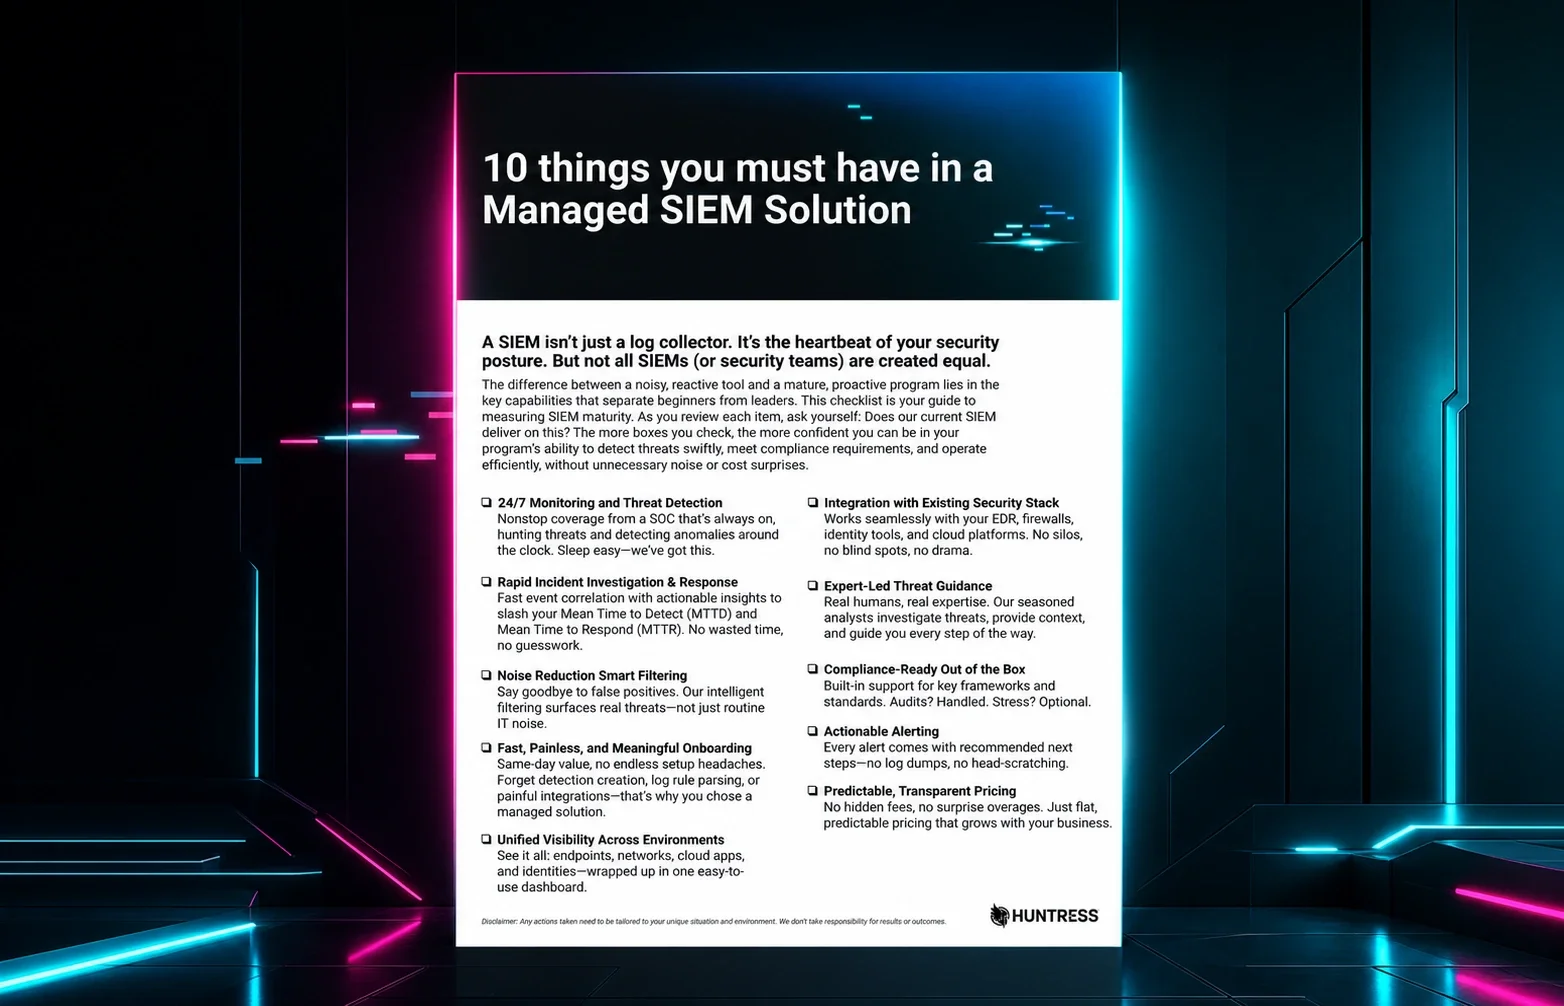
Download the guide and see why SIEM is a this-year decision.