Casey Smith

Casey Smith

Former Staff Threat Intelligence AnalystHuntress

Casey Smith's cybersecurity journey began in the early 2000s at Cisco Systems, where he contributed to the groundbreaking SAFE (Secure Architecture for Enterprise) initiative — sparking a career-long passion for testing the boundaries of defensive systems. He is the co-creator of Atomic Red Team, a widely adopted open-source testing framework, and has held impactful roles at Red Canary, Thinkst Canary, and in the financial sector. 

At Huntress, Casey focuses on adversary tactics with a keen interest in identity-based attacks. He's driven by a simple but powerful philosophy: if you haven't tested it, it doesn't work. When he's not outsmarting adversaries, Casey can be found exploring the Colorado outdoors or diving into a good non-fiction book.

Blog Posts By This Author

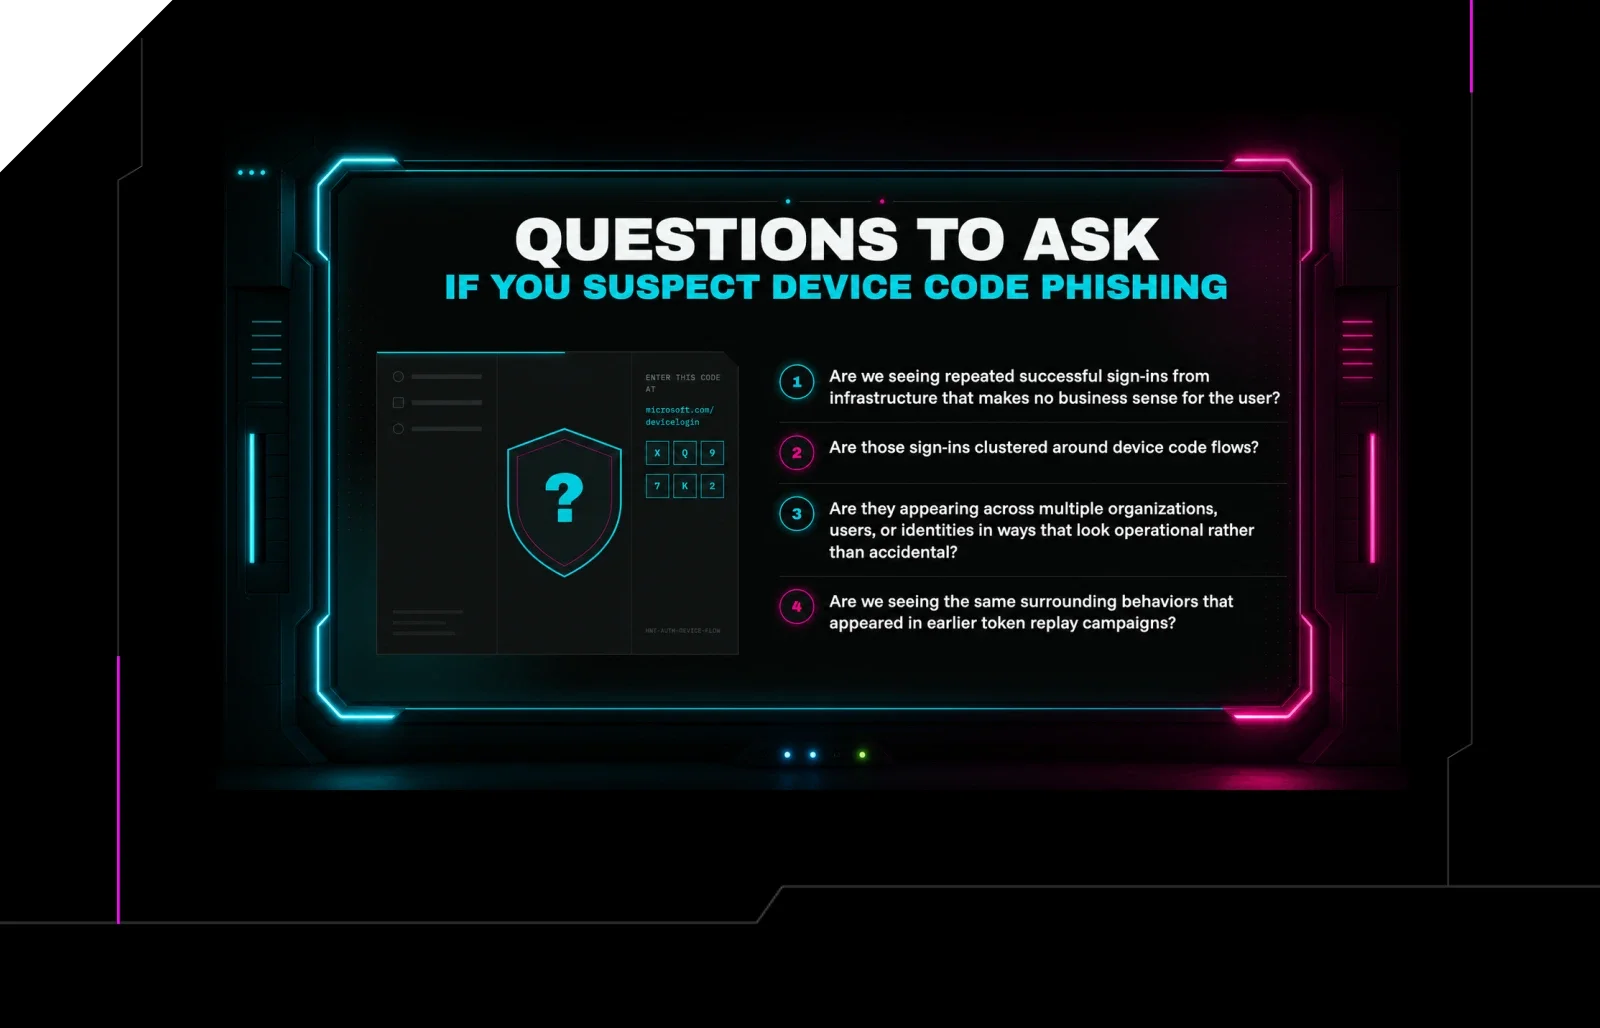
Read more about Microsoft 365 Device Code Phishing is Still Evolving: Railway, BL Networks, and More
Microsoft 365 Device Code Phishing is Still Evolving: Railway, BL Networks, and More
Blog Post

Huntress is tracking an evolving wave of device code phishing that abuses trusted Microsoft 365 sign-in flows. Learn the signals defenders should watch for and how to respond.

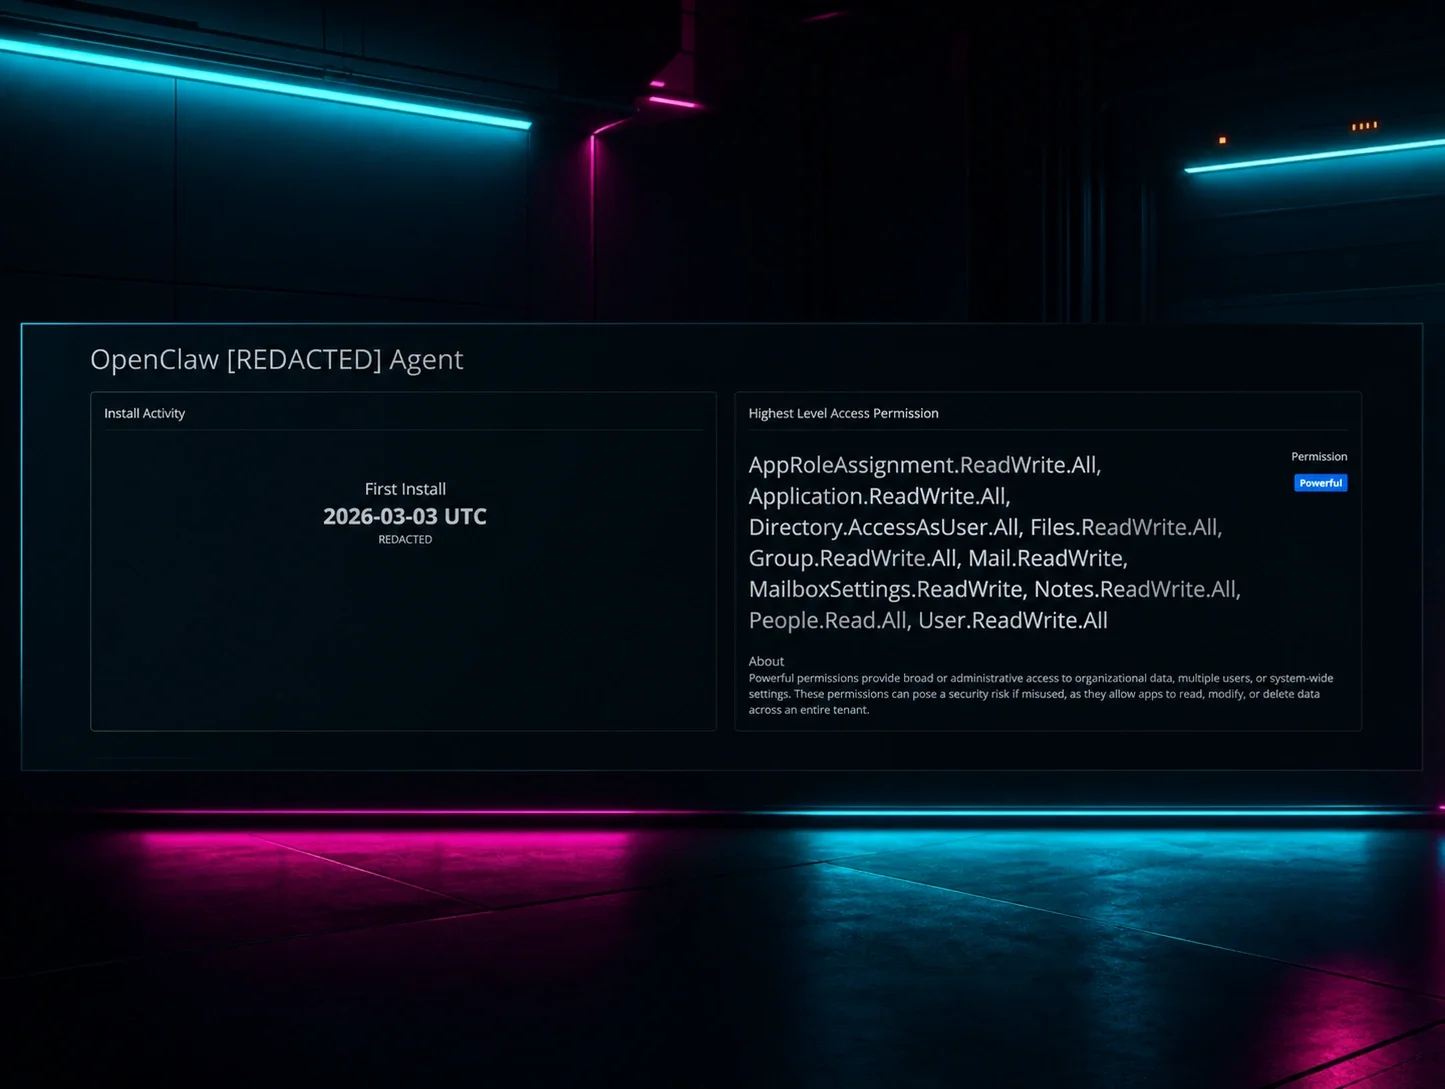
Read more about OpenClaw, Rogue Agents, and Application Hygiene
OpenClaw, Rogue Agents, and Application Hygiene
Blog Post

OpenClaw AI agents pose a security risk in Microsoft tenants because they're often granted broad, high-impact cloud permissions that an attacker could immediately inherit if the agent is compromised. Learn why proactive application hygiene, which includes continuous monitoring and trimming unnecessary permissions, is essential for managing this identity-based threat.