




Cybersecurity 101
Vulnerability Management Lifecycle: Steps and Best Practices
Learn the steps in vulnerability management, how to assess and prioritize risks, the best tools, and tips for a strong vulnerability management lifecycle.
What Is ESPM (Endpoint Security Posture Management)?
Written by: Lizzie Danielson
Published: 11/21/2025
Last Updated: 10/14/2026
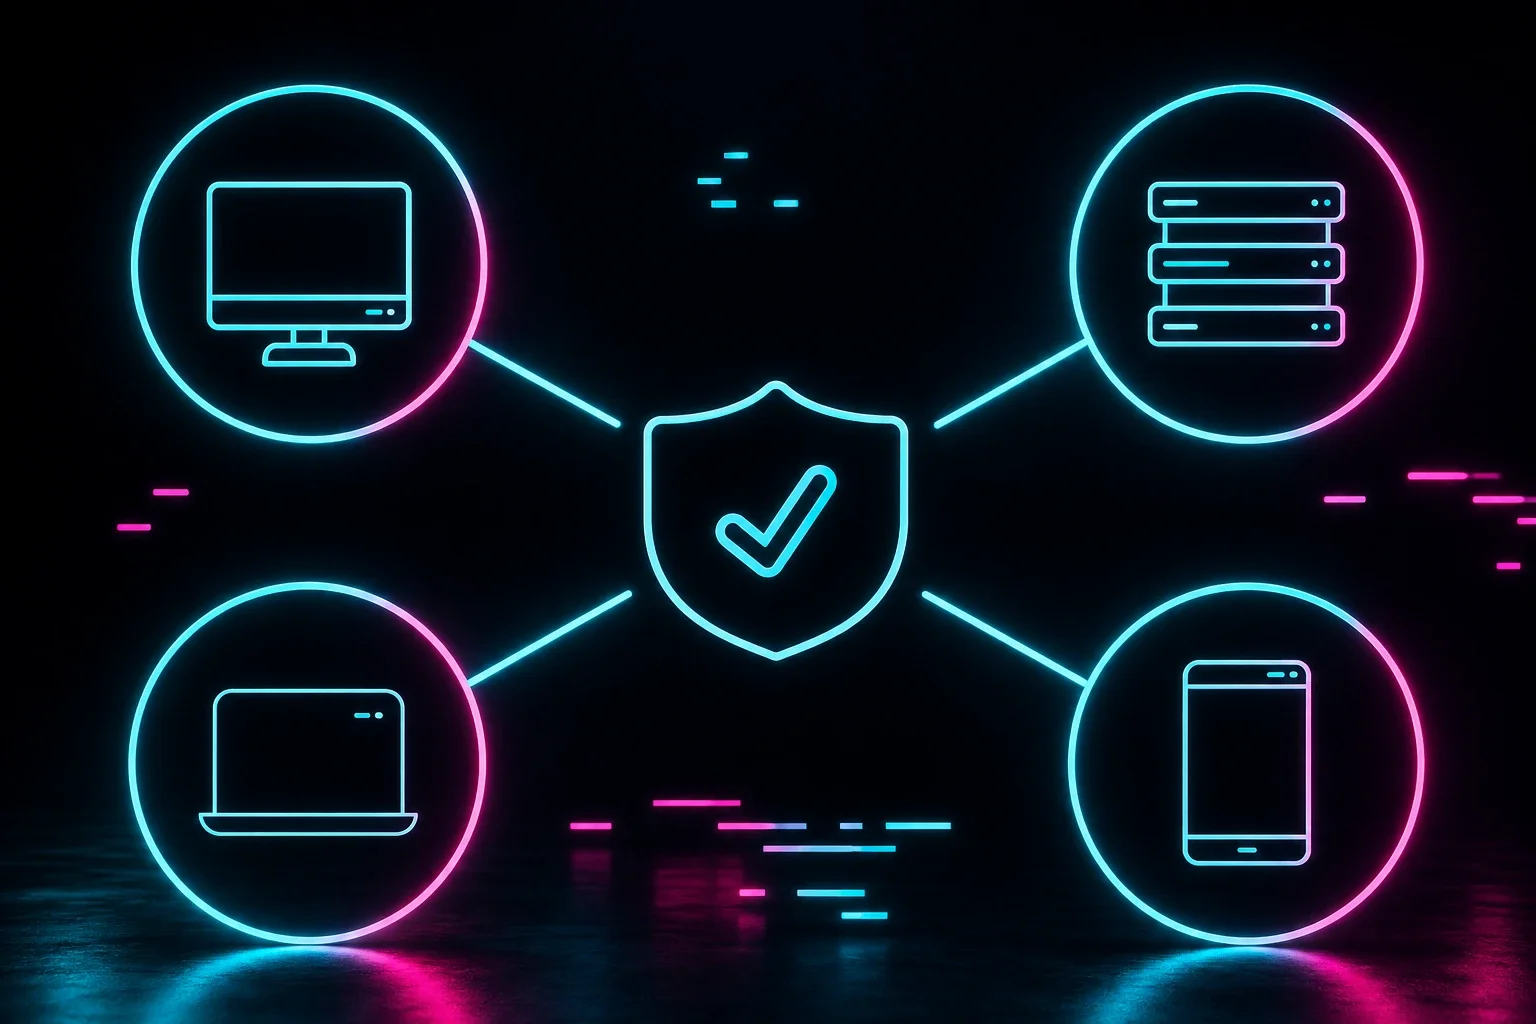
ESPM—or Endpoint Security Posture Management—is a continuous, automated audit of every device connected to your network.
Its job is to find "posture" weaknesses. Think: risky settings, missing updates, or security gaps on any laptop, server, or mobile phone.
Why care? Because endpoints are the frontline of cybersecurity. A single unpatched laptop or a misconfigured server is a wide-open invitation for an attacker to bypass your defenses and gain access to your entire network.
ESPM is a continuous, automated audit of every managed endpoint that replaces manual checklists and guesswork with real-time visibility into endpoint security health — identifying risks like missing patches, disabled firewalls, encryption gaps, and risky configurations before attackers can exploit them.
Endpoints are the frontline of cybersecurity, and device sprawl across laptops, remote desktops, cloud servers, and mobile phones makes it nearly impossible for IT teams to maintain a clear picture of their attack surface without an automated solution like ESPM.
ESPM is distinctly proactive, not reactive — unlike Antivirus (which blocks known malware) or Endpoint Detection and Response (EDR) (which detects active threats and suspicious behavior), ESPM focuses exclusively on hardening the endpoint's configuration and state to close security gaps before a breach occurs, like knowing which applications are running on endpoints and blocking the ones that can increase an endpoint’s attack surface.
A complete endpoint security strategy requires all three layers — AV to catch low-hanging fruit, ESPM to proactively harden devices, and EDR to detect advanced attackers who manage to get through. ESPM is the first pillar of comprehensive endpoint security, working alongside AV and EDR.
Device sprawl is a real problem. Your organization's data is accessed across laptops, remote workers' desktops, cloud servers, and mobile phones — many of which sit outside your direct line of sight.
This makes it nearly impossible for IT and security teams to maintain a clear, real-time picture of their attack surface. Did that remote employee actually install the latest security patch? Is the new server configured correctly? Is a user trying to install a printer driver that’s really an infostealer? Does every laptop have its firewall enabled and its antivirus running?
That uncertainty is risk. And in cybersecurity, uncertainty is exactly what attackers rely on.
Managed ESPM cuts through that chaos. It replaces manual checklists and guesswork with 24/7 visibility and control of your endpoint security health—giving your team the insights needed to know exactly how your endpoint security posture is at any moment, and be able to prove it to internal stakeholders and external parties.
ESPM is built around finding and fixing the "unforced errors" in your security posture. It's a proactive hardening tool, not a reactive one.
An ESPM solution continuously scans your devices and compares their current state against established security best practices and benchmarks. It's designed to surface common, but dangerous endpoint risks that often go undetected, including:
Missing patches: Laptops or servers are left vulnerable to known exploits because they're behind on critical software updates.
Security tool gaps: Workstations where the antivirus is disabled, the EDR agent has gone offline, or the host firewall has been turned off.
Risky configurations: ESPM also enforces practical application control, preventing unapproved or risky applications from running on endpoints in the first place
Encryption gaps: Mobile phones or laptops with access to company data that don't have disk encryption enabled.
Unauthorized software: Risky or unapproved applications like RMMs tools installed on company devices without IT awareness.
Each one of these represents a real, exploitable gap in your defenses. ESPM finds them systematically, continuously, and without depending on your team to manually go looking.
This is one of the most important distinctions in endpoint security—because these tools serve fundamentally different purposes. Together, they form the pillars of a complete endpoint security strategy, consistent with frameworks like theNIST Cybersecurity Framework.
Antivirus (AV): Your baseline protection. AV scans for known malware signatures—think of it as a digital "Most Wanted" list. If a file matches a known threat, it's blocked. It's reactive and signature-based, and while essential, it's not designed to catch what it doesn't already recognize.
EDR: Your active threat hunter. EDR goes beyond known bad files and watches for suspicious behavior—flagging a legitimate tool like PowerShell being used in a malicious way. EDR is built for detecting and responding to active breaches, including sophisticated attacks that slip past AV.
ESPM (Endpoint Security Posture Management): Your proactive hardener. ESPM doesn't look for active attacks or malicious files. Instead, it inspects the configuration and state of the endpoint itself finding the unauthorized applications, missing patches, the disabled firewalls, and the bad settings before an attacker ever gets the chance to exploit them.
The key insight is this: for a resilient security program you need all three working together. AV stops the low-hanging fruit. ESPM hardens the endpoint so attackers have less to exploit in the first place. And EDR catches the advanced attacker who manages to get in anyway.
Relying on detection and response alone without proactively managing your endpoint posture, means you're always playing catch-up. ESPM shifts the balance in your favor.
Cybersecurity resilience isn't just about stopping attacks—it's about reducing your attack surface so that fewer attacks succeed, and recovering faster when they do.
ESPM directly builds that resilience by:
Shrinking the attack surface continuously. Rather than waiting for a quarterly audit or a breach to reveal gaps, ESPM helps close exposures – like vulnerabilities and unexpected apps – in real time, before attackers have a window to act.
Giving teams hard data, not guesswork. Security teams can prioritize remediation based on real risk exposure rather than assumptions—making every hour of effort count more.
Supporting compliance and audit readiness. Continuous posture visibility means you can demonstrate the security health of your environment at any time, not just when an auditor asks.
Removing implementation and management overhead. For organizations without large, dedicated security teams, a managed ESPM solution ensures posture hardening happens consistently, without requiring the expertise or headcount of an enterprise security operation.
The result is an environment that's fundamentally harder to attack, and a security team that's always ahead of the curve rather than reacting to the last incident.
Detection and response are essential, but it's not enough on its own. If your endpoints have misconfigured settings, disabled security tools, or unpatched vulnerabilities, you're handing attackers a head start before your EDR even has a chance to respond.
That's why Huntress pairs its enterprise-grade Managed EDR with Managed ESPM—giving you both pillars of a complete, resilient endpoint security strategy in one solution built specifically for organizations without enterprise-sized security teams or budgets.
Huntress Managed ESPM continuously audits your endpoint attack surface, finds the gaps that make breaches possible, and removes the implementation and management complexity that makes posture hardening impractical for most teams. It doesn't just provide data, it provides managed action, so your environment gets harder to attack without adding burden to your team.
Huntress Managed EDR then watches over that hardened environment 24/7, with a Security Operations Center actively hunting for the threats that still try to get through.
Together, they work as the first and second line of defense:
ESPM proactively closes the gaps attackers would otherwise exploit.
EDR actively detects and responds to the sophisticated threats that attempt to breach your defenses anyway.
Unlike complex enterprise platforms built for large security teams with deep budgets, Huntress delivers both capabilities in a managed model—purpose-built for MSPs and mid-market organizations who need real protection without the overhead.
Stop guessing about the security health of your endpoints.
ESPM | EDR | MDR | |
|---|---|---|---|
Full name | Endpoint Security Posture Management | Endpoint Detection and Response | Managed Detection and Response |
What it focuses on | The security configuration and state of endpoints | Endpoint activity and behavior that may signal an attack | Ongoing security monitoring, investigation, and response, typically delivered by a provider's security team |
Primary question | Are our endpoints configured and protected as they should be? | Is suspicious or malicious activity happening on an endpoint? | Who is monitoring security signals and helping investigate and respond to threats? |
Main role | Reduce exposure by identifying and helping remediate posture gaps | Detect, investigate, and contain threats on endpoints | Provide people and processes to monitor, investigate, and respond to threats using security tools and telemetry |
Examples | Finding missing patches, disabled firewalls, gaps in encryption, or risky/unauthorized applications | Detecting suspicious process behavior, investigating activity, and isolating a compromised endpoint | 24/7 alert monitoring, threat investigation, escalation, and response coordination |
What it is | A security capability or toolset | A security capability or toolset | A managed service; it may include or rely on EDR and other security tools |
In short: ESPM helps harden endpoints before an attack. EDR helps detect and respond to malicious activity on endpoints. MDR provides a security team to monitor, investigate, and respond using tools like EDR. They're complementary, not interchangeable.
ESPM evaluates endpoints against a baseline of security controls and surfaces specific failures — not risk scores, not vague warnings. Here's what it actually finds in real environments:
Encryption disabled. BitLocker or FileVault not enabled on endpoints. A lost or stolen laptop means every file on it is accessible to anyone who picks it up. The NSA's BitLocker Guidance and NIST SP 800-171 (Control 3.13.11) both treat encryption at rest as a baseline requirement — not optional.
Endpoint protection turned off. Windows Defender real-time protection disabled — sometimes by users who found it inconvenient, sometimes by malware that shut it down before running. Defense tampering — including disabling Defender — is documented in the Huntress 2025 Cyber Threat Report as standard attacker behavior, not an edge case.
Unpatched software with known vulnerabilities. Applications running with publicly documented critical CVEs. According to the Verizon 2025 Data Breach Investigations Report, vulnerability exploitation rose to the #2 initial access vector at 20% of breaches — a 34% year-over-year increase.
AutoRun enabled. Any USB drive plugged into the machine can execute code automatically on connection. CISA explicitly recommends disabling AutoRun to prevent malicious USB-based code execution — a risk documented since the Conficker worm's mass spread via infected USB drives.
Weak local administrator credentials. Local admin accounts with default or simple passwords. NSA and CISA identified default credentials and shared local admin passwords as the #1 most common misconfiguration across 1,000+ federal network assessments — and the primary enabler of lateral movement via credential reuse.
RDP exposed to the internet. Remote Desktop Protocol accessible without additional controls. According to the Microsoft Digital Defense Report 2024, RDP access accounts for 53% of offerings sold by access brokers — making it the most traded initial access commodity in the cybercrime economy.
Unmanaged endpoints. Security software not installed or not reporting in. Microsoft's research found that 80–90% of successful ransomware compromises originate through unmanaged devices — endpoints on the network but outside IT's visibility.
For MSPs, ESPM findings translate directly into client conversations. Instead of abstract risk discussions, you can show a specific list of specific issues on specific machines. "Three of your 20 endpoints have encryption disabled" is concrete and actionable — the kind of detail that makes quarterly business reviews productive. Security posture becomes a scorecard with measurable improvement over time rather than a vague concept you have to sell.
Additional Resources
Learn the steps in vulnerability management, how to assess and prioritize risks, the best tools, and tips for a strong vulnerability management lifecycle.
Learn how fileless malware works, why it's so effective, and essential strategies to detect and prevent these memory-based cyberattacks.
Learn AWS cloud security fundamentals, shared responsibility model, key features like encryption & IAM, plus best practices for cybersecurity professionals.

